VPN Connet
VPN Connet


Document

- Documentation
 VPN ConnetBest PracticesConnections between virtual private clouds and data centersIPsec-VPN connection via VPN gatewayConnecting a VPC to multiple data centers via IPsec-VPN connection with static routing
 Copy page
 Download PDF
IPsec-VPN connection via VPN gateway
Connecting a VPC to multiple data centers via IPsec-VPN connection with static routing
Copy pageDownload PDFConnecting a VPC to multiple data centers via IPsec-VPN connection with static routing
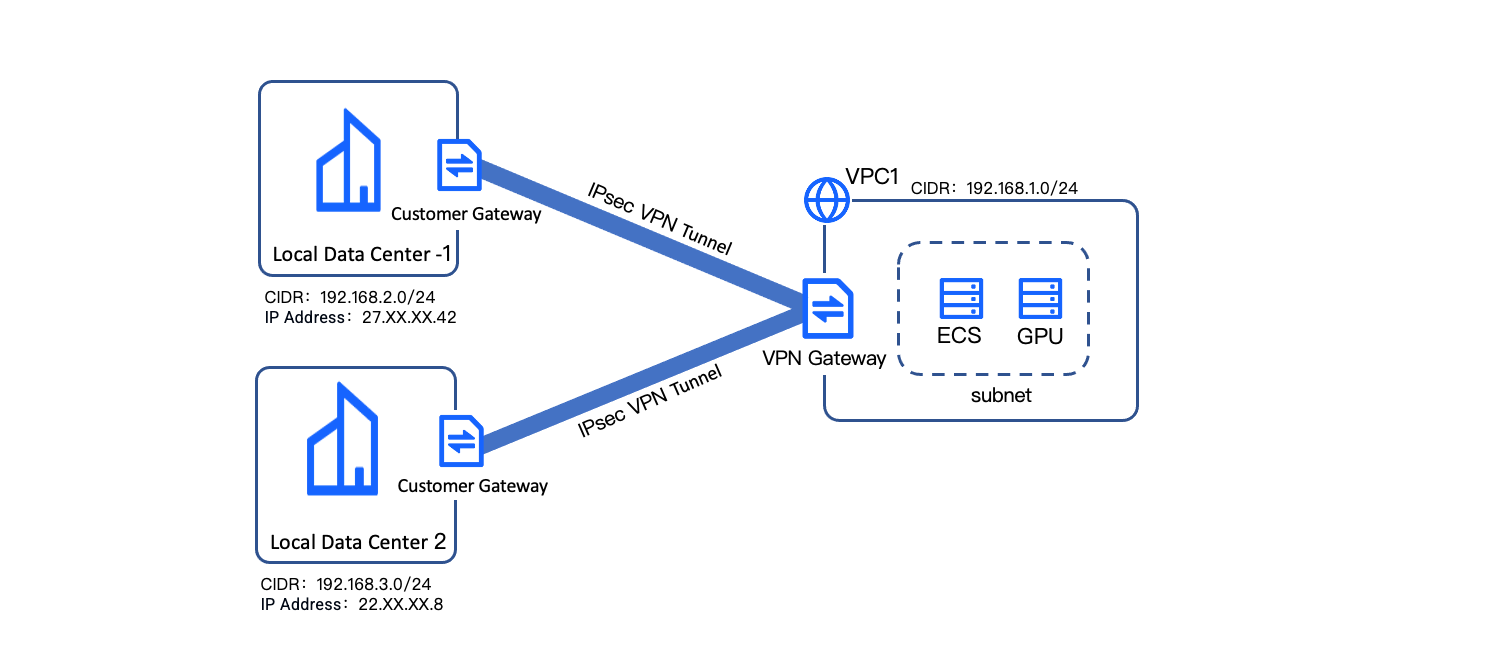
This topic introduces how to establish IPsec-VPN communication tunnels in static routing mode between a Virtual Private Cloud (VPC) and multiple on-premises data centers (IDC) using the IPsec-VPN connection feature. These tunnels enable flexible hybrid cloud deployment solutions.
Prerequisites
- Create VPC1 and its subnet. For proceduer, see Creating a VPC.
- The gateways of on-premises IDC1 and IDC2 both have static Elastic IP Addresses (EIPs).
- The CIDR blocks of on-premises IDC1 and IDC2 do not overlap with each other or with the private CIDR block of VPC1.
Related information
tip
If two IDCs in the same region establish VPN connections with the cloud VPC, the operations are the same as described here.
The obtained information is shown below. VPC1 and its subnet, as well as ECS cloud servers and GPU cloud servers, are created cloud resources. The VPN gateway and customer gateway are resources to be created in subsequent operations.
Procedure
Step 1: Create a VPN gateway
- Log in to the VPN gateway console.
- In the top menu bar, select the target project Project-02 and target region China (Beijing).
- Click Create VPN Gateway and configure the VPN gateway parameters based on the table below.
- ParameterDescriptionSample valueBasic informationBilling methodThe billing method for the VPN gateway.SubscriptionNameName of the VPN gateway.VPNGW-testTunnel modeThe tunnel mode of the VPN gateway.Single tunnelNetwork ConfigurationMaximum bandwidthSet the bandwidth cap for the VPN gateway.This value is the bandwidth shared for all IPsec-VPN connections and SSL-VPN connections created on this VPN gateway.20MbpsVPCThe VPC where the VPN gateway resides.VPC1 | 192.168.1.0/24SubnetSelect the subnet where the VPN gateway resides. Reserve enough IPv4 addresses in the subnet for deploying the VPN gateway.Subnet1|192.168.1.128/25BGP ASNSet the Autonomous System Number (ASN) for the VPN gateway. Configuring BGP ASN for a VPN gateway is only required for an IPsec-VPN connection in dynamic routing mode. This example uses static routing, so BGP ASN configuration is not required.--Function configurationIPsec-VPN capabilityEnable IPsec connectivity as needed. After enabling, you can use the IPsec-VPN feature and can enable SSL connectivity concurrently.CheckSSL-VPN capabilityEnable SSL connectivity as needed. After enabling, you can use the SSL-VPN feature and can enable IPsec connectivity concurrently.DisabledMore informationDurationThe validity period for which the VPN gateway is subscribed.1 monthAutomatic renewalEnable automatic renewal as needed.DisableAffiliated ProjectThe resource’s project is fixed to the project Project-02 selected before entering the creation page. Cloud resources cannot be shared between different projects.Project-02
- Click Confirm order, and follow the console guidance to review and accept the legal terms.
- Click Buy now to complete your purchase. Click Confirm order and follow the interface prompts to finish.
- After successfully creating the VPN gateway VPNGW-test, the system assigns the gateway egress IP as 180.XX.XX.91.
Step 2: Create a customer gateway
- Log in to the Customer Gateway console.
- In the top menu bar, select the target project Project-02 and target region China (Beijing).
- Click Create Customer Gateway.
- Configure the customer gateway based on the table below, and click Confirm when completed.
- ParameterDescriptionSample valueRegionsSelect the region where the customer gateway resides. The customer gateway must reside in the same region as the Virtual Private Cloud (VPC1) and the VPN gateway (VPNGW-test).China (Beijing)NameSet the name for the customer gateway.CGW-01IP AddressType the static public IP address of the peer VPN gateway, which is the gateway’s egress IP address.27.XX.XX.42BGP ASNSet the ASN (Autonomous System Number) for the customer gateway. Configuring BGP ASN for a customer gateway is only required for an IPsec-VPN connection in dynamic routing mode. This example uses static routing, so BGP ASN configuration is not required.--Affiliated ProjectThe customer gateway's project is fixed to the project Project-02 selected before entering the creation page.Project-02
- Follow steps 2 to 4 to create another customer gateway CGW-02, select region China (Beijing), and set the IP address to 22.XX.XX.8.
Step 3: Create an IPsec-VPN connection
- Log in to the VPN Connection console.
- In the top menu bar, select the target project Project-02 and region China (Beijing).
- Click Create VPN Connection.
- Configure the IPsec-VPN connection based on the table below, and click Create after completing the configuration.
- Basic information
- ParameterDescriptionSample valueRegionsSelect the region where the IPsec-VPN connection is located.China (Beijing)NameName of the IPsec-VPN connection.IPsecVPN-01Affiliated ProjectThe project of the resource. Fixed as Project-02 selected before entering the creation page.Project-02
- Associate resources
-
- Connection information
-
- Repeat steps 2 to 4 to create IPsecVPN-02. Select the region China (Beijing), choose VPN gateway VPNGW-test, and set the pre-shared key to test@321.
Step 4: Configure VPN gateway routing
- Log in to the VPN gateway console.
- In the top menu bar, select the target project (Project-02) and target region (China (Beijing)).
- Click the VPN gateway name VPNGW-test in the list to enter the details page.
- Select the Routing information tab, then click Add route.
- Configure the route according to the table below.
- ParameterDescriptionSample valueDestination CIDREnter the private network segment of local IDC1.192.168.2.0/24Next Hop typeFixed to IPsec-VPN connection.IPsec-VPN connectionNext HopSelect IPsecVPN-01.IPsecVPN-01
- Click Confirm to add the route entry for Local IDC1 in VPNGW-test.
- Click Add route again, then configure route parameters according to the table below.
- ParameterDescriptionSample valueDestination CIDREnter the private network segment of local IDC2.192.168.3.0/24Next Hop typeFixed to IPsec-VPN connection.IPsec-VPN connectionNext HopSelect IPsecVPN-02.IPsecVPN-02
- Click OK to add the Data Center 2 route entry for VPNGW-test.
Step 5: Configuring the local gateway route
The configuration method for IPsec-VPN varies slightly among different gateway devices. Both IDC1 and IDC2 introduced here use Sangfor firewalls. Configure IDC gateway routes separately. For details, refer to Configuring Sangfor firewall.
After completing route configuration, the VPN connection setup is finished. At this point, local IDC1 and IDC2 can connect through the IPsec tunnel to access cloud servers in VPC1.
Last updated: 2026.07.15 18:21:42
All rights reserved © Beijing Volcano Engine Technology Co., Ltd2024
