Load Balancer
Load Balancer
Load Balancer


Document
Announcement
Network Load Balancer (NLB)
What's New
Product Description
Quick Start
User Guide
NLB instances
Server Group
Listeners
Projects and Tags
Best Practices
Cross-VPC Backend Server
API
NLB Instance
Listener
Server group
TLS Security Policy
SDK Reference
Application Load Balancer (ALB)
Updates and Announcements
Overview
Getting Started
User Guide
Instance
Listeners
Creating a listener
Forwarding rules
Server groups
Manage certificates
Security management
Logs and monitoring
Application of ALB in VKE
Resource management
Project-based management
Tag-based management
API Reference
ALB Instance
Availability Zone
Listener
server group
Health Check Template
forwarding rules
certificate
access log interface
Health Check Log
access control
personalized configuration
Best Practices
FAQs
Classic Load Balancer (CLB)
Overview
Product billing
Quick Start
User Guide
CLB instances
Backend Server Group
Listener
Creating a listener
Configuring a forwarding rule
Certificate management
Logs and monitoring
Identity and Access Management
Projects and Tags
Best Practices
Creating a static page
Configuration practice of a forwarding rule
Disaster Recovery Best Practices
Obtaining the client source IP address
API reference
CLB instances
Listener
Backend server group
ACL
Forwarding rule
Certificate
Access log (Layer-7)
Health check log
SDK Reference
- Documentation
 Load BalancerNetwork Load Balancer (NLB)User GuideNLB instancesConfiguring the security group and Network ACL for NLB
 Copy page
 Download PDF
NLB instances
Configuring the security group and Network ACL for NLB
Copy pageDownload PDFConfiguring the security group and Network ACL for NLB
Scenarios
To ensure that the NLB instance functions properly, both the NLB instance and backend server must have security groups and Network ACs to allow necessary traffic. This article explains how to allow the necessary traffic for the NLB instance's security group and Network Access Control List.
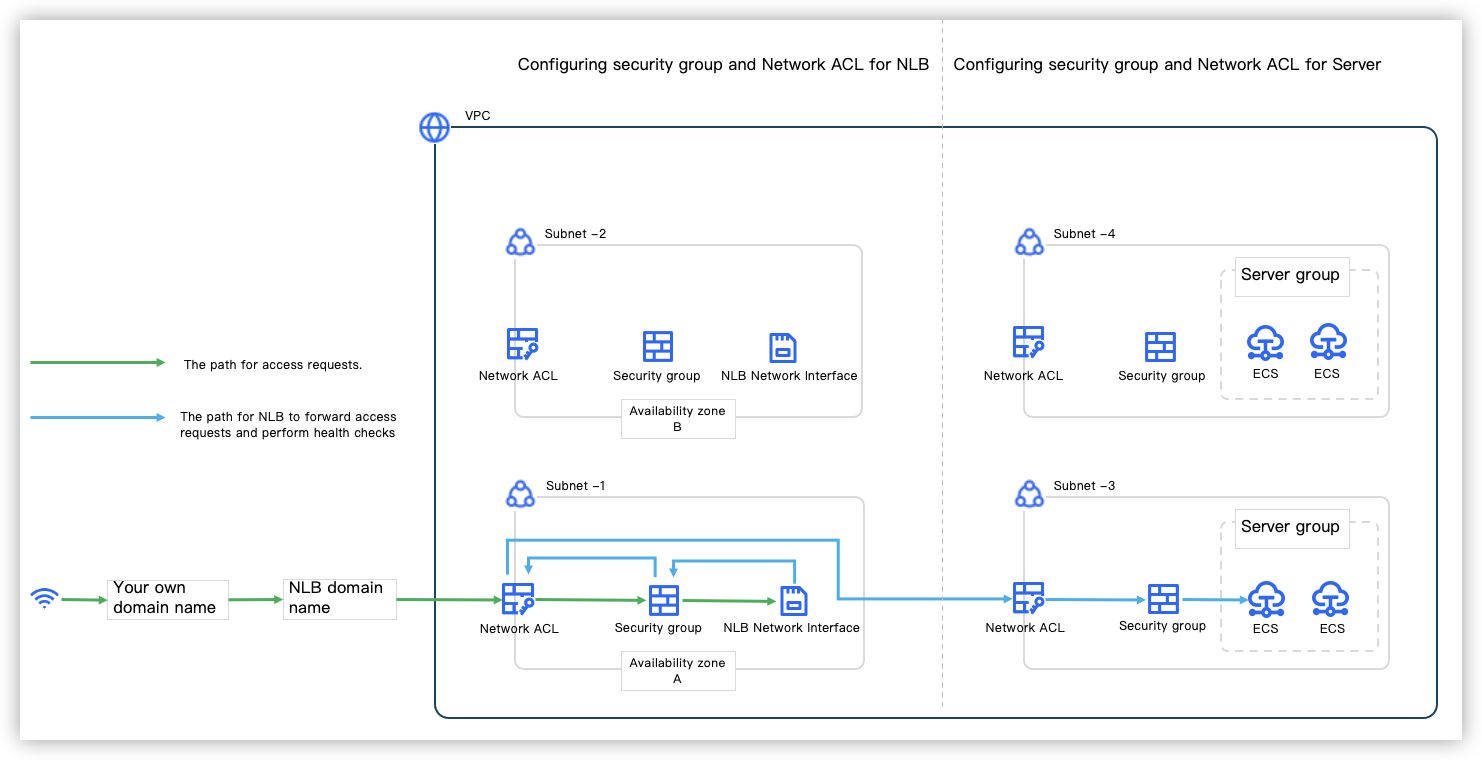
For information on configuring the security groups and network ACLs of backend servers to allow relevant traffic, see Configuring the security group and network ACLs for backend servers.
Configuration instructions
Security groups are stateful. Return Traffic: Return data flows are automatically permitted and are not affected by these rules.
Network ACL is stateless. Return traffic must be explicitly allowed by rules, meaning that both outbound and inbound directions must be explicitly permitted by the rules.
The requirements for allowing traffic in the security group and Network Access Control List associated with the NLB instance are as follows:
Security groups and Network Access Control List (ACL) | | Traffic Configuration Guide (The traffic descriptions below include the corresponding return data flows) |
Security group | |
For ease of configuration and management, it is recommended to allow all outbound traffic. |
Network ACL | NLB instances and backend servers belong to same subnets | Network ACL inbound and outbound rules must allow the following traffic (outbound rules are recommended to allow 0.0.0.0/0):
Since the NLB and backend servers belong to the same subnet, the following traffic bypasses the network ACL and does not require network ACL configuration:
For ease of configuration and management, it is recommended to allow all outbound traffic. |
| NLB instances and backend servers belong to different subnets | Network ACL inbound and outbound rules must allow the following traffic:
For ease of configuration and management, it is recommended to allow all outbound traffic. |
Configuration examples
tip
For IPv4 NLB instances, no IPv6 traffic allowance rules are required as below.
Security group
- Only allow specific IP addresses to access NLB
- DirectionPriorityStrategyProtocol typePort rangeSource/destination addressDescriptionInbound1AllowALLListening portClient IP addressAllow inbound client traffic to the NLB1AllowICMPALL100.64.0.0/10Allow traffic to detect the availability of the NLB instance private IPv4 address1AllowICMPV6ALLfd00:64::/32Allow the traffic probing the availability of the private IPv6 address of the NLB instance100DenyALLALL0.0.0.0/0Deny-all fallback policyOutbound100AllowALLALL0.0.0.0/0Allow-all fallback policy
- Reject specific IP addresses from accessing NLB
- DirectionPriorityStrategyProtocol typePort rangeSourceDescriptionInbound1DenyALLListening portAccess to the NLB's IP address is not allowedDeny specified IP addresses from accessing the NLB
Network ACL
- The backend server is in the same subnet as the NLB
- Rule directionPriorityStrategyAgreementSource/destination addressDestination portDescriptionInbound1AllowListening protocolClient IP addressListening portAllow inbound client traffic to the NLB2AllowICMP100.64.0.0/10ALLAllow traffic for system probes to detect the availability of the NLB private IPv4 address3AllowICMPV6fd00:64::/32ALLAllow traffic for system probes to detect the availability of the NLB private IPv6 addressOutbound1AllowALL0.0.0.0/0ALLAllow all IPv4 traffic2AllowALL::/0ALLAllow all IPv6 traffic
- The backend server is in a different subnet from the NLB
- Rule directionPriorityStrategyAgreementSource/destination addressDestination portDescriptionInbound1AllowListening protocolClient IP addressListening portAllow client access traffic2AllowHealth check protocolBackend server private IP addressHealth check portAllow the health check response traffic from backend server to the NLB3AllowListening protocolBackend server private IP addressBackend server portAllow the client's response traffic from backend server to the NLB4AllowICMP100.64.0.0/10ALLAllow traffic for system probes to detect the availability of the NLB private IPv4 address5AllowICMPV6fd00:64::/32ALLAllow traffic for system probes to detect the availability of the NLB private IPv6 addressOutbound1AllowALL0.0.0.0/0ALLAllow all IPv4 traffic2AllowALL::/0ALLAllow all IPv6 traffic
Last updated: 2026.06.12 15:23:50
All rights reserved © Beijing Volcano Engine Technology Co., Ltd2024
