Torch Object Storage
Torch Object Storage
Torch Object Storage


Document
What's New
Announcements
Billing
Billable items
Billing method
Getting Started
User Guide
Working with buckets
Basic configurations
Managing lifecycle
Back-to-origin rules
Event notification
Intelligent Tiering
Domain management
Fault tolerance and disaster recovery
Cross-region replication
Same-region replication
Data redundancy
Image processing
ObjectSet
Working with objects
Managing folders
Monitoring and alerting
Metric monitoring
Access control
Bucket policies
Common configuration scenarios
Authorizing IAM users of the current account
Authorizing other accounts
Managing access via tools and SDKs
Managing public read access
Data security
Access points
Multi-region access points (MRAP)
Single-region access points (SRAP)
Converged access points (CAP)
DevMind
TOS accelerator
SenseFlow
TOS Agent
Data processing
Basic concepts
Image processing
Media processing
Document preview
Task processing
Data subscription
Flow control management
Quality of Service (QoS) policies
Hierarchical namespace (HNS)
User guide
Tool reference
Best practices
TOS Vectors
User guide
API reference
Vector bucket
Vector index
SDK reference
Python-Vectors
Vector bucket
Vector index
Java-Vectors
Vector bucket
Vector index
Node.js-Vectors
Vector bucket
Vector index
Tool Guide
tosutil
Common commands
Upload, download, and copy objects
Share objects
Auxiliary commands
Common examples
TOS Browser
FSX
FSX best practices
TOS PyTorch Connector
tosfsspec
TOS Import(will be deprecated soon)
API Reference
Signature Mechanism
The header contains a signature
Bucket
Basic Bucket Operations
Bucket Lifecycle
Access Monitor
Bucket ACL
Bucket CORS
Bucket Policy
Back-to-origin Rules
Bucket Replication
Versioning
Static Website
Event Notification
Custom Domain
Server-side encryption
Transfer Acceleration
Data Processing
Image processing
Media processing
Video transcoding
Audio transcoding
video to GIF
Document preview
File decompression
Log Storage
Retention Policy
Requester pays
TLS version
Object
Basic Object Operations
Object ACL
Fetch Object
Symbolic Link
WORM object
Multipart Upload
SDK Reference
Java
Pre-signing Mechanism
Bucket Interface
Basic Bucket Interface
Manage Bucket Configuration
Object Interface
Upload Object
Download Object
Upload and Download Speed Limit
Copy Object
List Object
Data Processing
Image Processing
Video Processing
Audio Processing
Log Configuration
Hierarchical Namespace
Bucket base interface
Introduction to Typical Scenes
Python
Data processing
Pre-signature mechanism
Bucket interface
Basic bucket interface
Manage bucket configuration
Object interface
Upload object
Download object
Copy object
List objects
Introduction to typical scenes
C
Object Interface
Upload object
C++
Pre-signature Mechanism
Bucket Interface
Basic Bucket Interface
Manage Bucket Configuration
Object Interface
Upload Object
Download Object
Copy Object
List Objects
Data Processing
Go
Object Interface
Upload Object
Download Object
Copy Object
List Objects
Manage Objects
Bucket Interface
Manage Bucket Configuration
Data Processing
Log Configuration
Introduction to Typical Scenes
Pre-signature Mechanism
Node.js
Pre-signature Mechanism
Bucket Interface
Basic Bucket Interface
Manage Bucket Configuration
Object Interface
Upload object
Download object
Copy object
List objects
Data Processing
Image Processing
Introduction to Typical Scenes
Browser.js
Pre-signature Mechanism
Upload Object
Download Object
Copy Object
List Objects
Manage Objects
Data Processing
.NET
Bucket Interface
Object Interface
Upload Object
Download Object
List Objects
Introduction to Typical Scenes
PHP
Bucket Interface
Object Interface
Download Object
Data Processing
Exception Handling
Android
Bucket Interface
Object Interface
Upload Object
Download Object
Exception Handling
iOS
Bucket Interface
Object Interface
Upload Object
Download Object
Harmony
Pre-signature Mechanism
Bucket Interface
Object Interface
Upload Object
Download Object
List Objects v2
Introduction to Typical Scenarios
Rust
Pre-signing mechanism
Bucket interface
Basic bucket operations
Lifecycle rules
Bucket ACLs
Cross-origin resource sharing
Bucket inventory
Back-to-origin rules
Bucket replication
Static website hosting
Event notification
Custom domain
Server-side encryption
Object interface
Basic operation
Access control
Error Codes
01-SERVICE_ERROR
02-AUTH
03-ACCESS_CONTROL
04-QOS
05-REQUEST
06-BUCKET
07-LIFECYCLE
08-ACL
09-CORS
10-POLICY
11-MIRROR
12-REPLICATION
13-WEBSITE
14-NOTIFICATION
15-ENCRYPT
16-CUSTOMDOMAIN
17-OBJECT
18-TAG
19-MULTIPART
20-STORAGE_CLASS
21-CALLBACK
22-DATA_PROCESS
23-BATCH
24-STORAGE_LENS
25-INVENTORY
26-DIRECTORY_BUCKET
FAQ
Best Practices
AIGC-Doubao LLMs
Accessing TOS with third-party tools
Granting temporary access
Data migration
Data processing
Checking data integrity
Performance optimization
- Documentation
 Torch Object StorageUser GuideAccess controlOverview
 Copy page
 Download PDF
Access control
Overview
Copy pageDownload PDFOverview
To ensure the security of your resources, TOS offers several authorization methods, including bucket policies, Identity and Access Management (IAM) policies, and access control lists (ACLs). Based on your business requirements, you can select the appropriate methods to allow different users to access or manage your resources.
Authorization methods
This topic provides the authorization methods supported by TOS and their use cases for your reference.
tip
- In general, we recommend that you configure permissions by using IAM policies or bucket policies.
- We also recommend that you select the same type of policies to facilitate further maintenance.
- If a configured permission does not take effect, we recommend that you retry later, as there is a delay.
Method | Principal | Action | Condition | Use cases |
IAM policy | IAM users | All. | Supported |
|
Bucket policy |
|
| ||
Bucket ACL |
|
| Not supported | When authorizing IAM users in another account or all users to read or write all objects in a bucket. tip Only an account can grant permissions to other accounts. |
Object ACL |
|
| Not supported | When granting permissions (private, public read, or public read/write) to a single object. |
Which method should I select?
The following table compares various authorization methods. Select the appropriate methods based on your business requirements.
Parameter | Type | Bucket policy | IAM policy | ACL |
Principal (authorized user) | IAM users within the same account | ✔️ | ✔️ | ❌ |
| Other accounts | ✔️ | ❌ | ✔️ |
| IAM users in another account | ✔️ | ❌ | ❌ |
| All users | ✔️ | ❌ | ✔️ |
Effect (action to take) | Allow | ✔️ | ✔️ | ✔️ |
| Deny | ✔️ | ✔️ | ❌ |
Resource (authorized resource) | All TOS resources | ❌ | ✔️ | ❌ |
| A TOS bucket | ✔️ | ✔️ | ✔️ |
| A group of specified TOS objects | ✔️ | ✔️ | ❌ |
| A TOS object | ✔️ | ✔️ | ✔️ |
Action | Service-level permissions (creating buckets or listing all buckets) | ❌ | ✔️ | ❌ |
| Specific permissions on buckets or objects | ✔️ | ✔️ | ❌ |
| Read/write permissions on buckets or objects | ✔️ | ✔️ | ✔️ |
Condition | Conditions for applying permissions | ✔️ | ✔️ | ❌ |
Which permission rule applies when they conflict?
Setting multiple permission rules may result in conflicts. The authorization process is as follows:
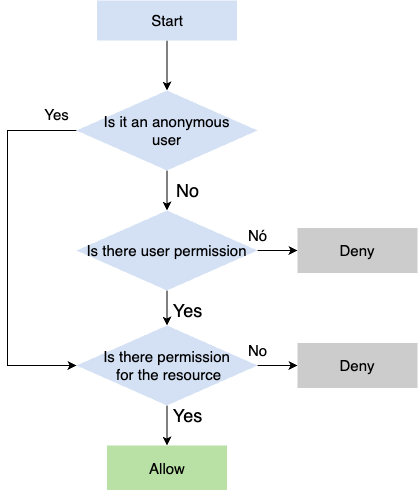
- Check whether all users are authorized.
- Yes: Go to Step 2.
- No: Check user permissions.
-
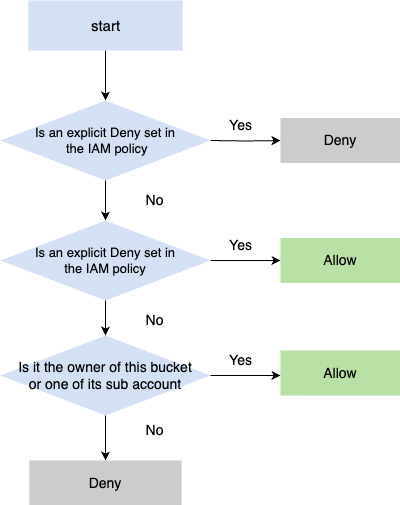
- If the check passes, check resource permissions.
warning
By default, the ACL permissions for the resource owner are set to Allow.
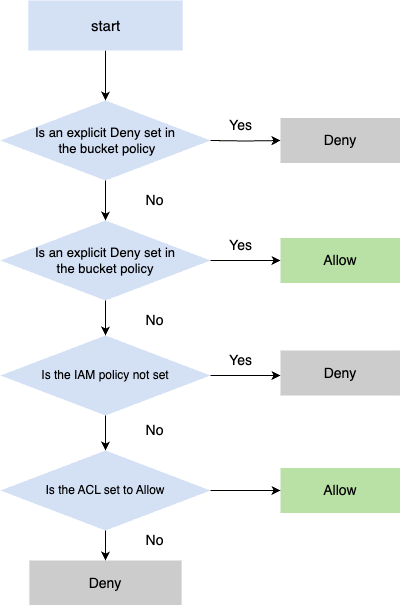
The following table describes which action (allow or deny) to take when there is a conflict between bucket policies, IAM policies, and ACLs for any bucket owner or their IAM users.
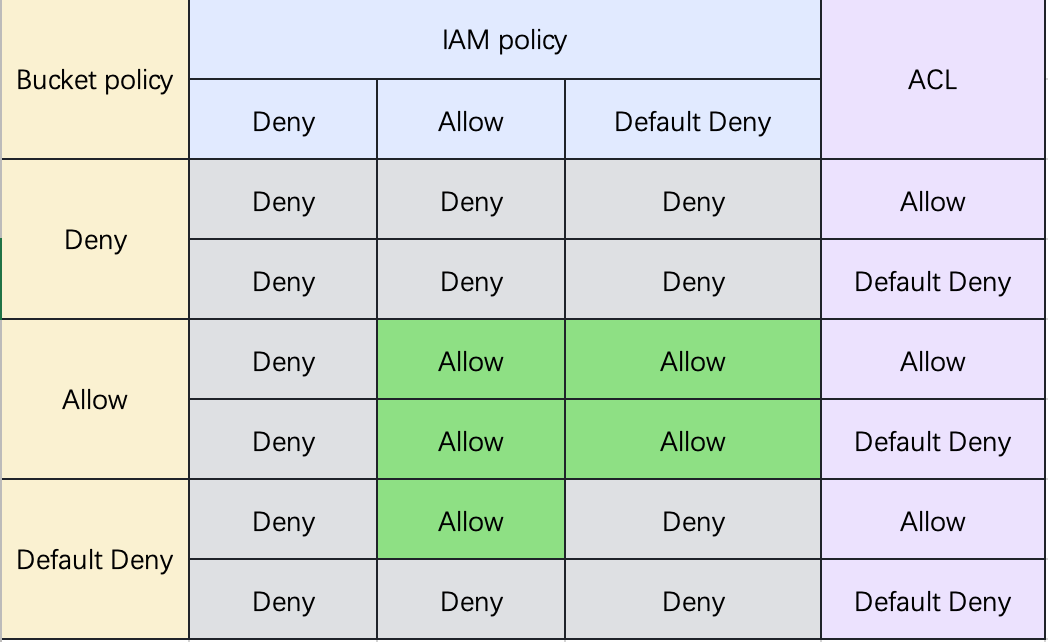
Related documentation
- ACLs
Last updated: 2026.01.04 11:15:05
All rights reserved © Beijing Volcano Engine Technology Co., Ltd2024
