Elastic Compute Service
Elastic Compute Service
Elastic Compute Service


Document
Elastic Compute Service
What's New
Announcement
OpenAPI related
Pricing and quotas are related
About products and plugins
Feature discontinuation
Overview
Billing
Billable items
Billing methods
Billing methods change
Getting Started
User Guide
Instances
Instance types
X86 Computing
Elastic Bare Metal Server
Heterogeneous Computing
Select instance billing method
Spot instance
Elastic Scheduled Instance
Offsetting Resources
Reserved Instances
Buying ECS instances
Logging in to an instance
Logging in to a Linux instance
Managing instance status
Modifying instance types
Using instance user data and metadata
Instance metadata
Images
Public images
veLinux images
Custom images
Importing custom images
Creating custom images
Image detection
End of life (EOL) of image
Elastic Block Storage
Basic volume operations
Partitioning and formatting a volume
Extending a volume
EBS Agent
Snapshots
Basic snapshot operations
Auto snapshot policies
DataInsights
Network
Network interface and IP address
IP Address
IPv4 address
Security group
Security
Passwords and key pairs
Deployment and scaling
Monitoring
Monitoring metrics
Event monitoring
Local volume event O&M
Method 1: Solve the local volume failure by replacing the faulty volume
O&M
Cloud assistant
Managing agents
Process choreography
Common operation and maintenance tasks
Batch operations on instances
Batch operations on EBS Volumes
Batch operations on images
Temporary upgrade of bandwidth
Managing application updates
orchestration plan
Patch management
Managing patch plans
Managing patch baselines
IAM
Tags and projects
Best Practices
AI applications
OpenClaw (formerly Moltbot)
Quickly deploying OpenClaw via application templates
Quickly deploying OpenClaw via marketplace images
Manually deploying OpenClaw
Self-service website creation
Building environments
Building a Web environment (Windows)
Building applications
Building FTP site
Deploying databases
Building game servers
Building websites
Building a WordPress blog
Building multiple websites
Manage software sources for Linux instances
AIGC practices
Performance test
Network performance test
Instance configuration
Setting up AD Domain Services on Windows OS
Windows Multi - User Login
Changing screen resolution
Instance data
Uploading or downloading files
Data restoration
ECS instance local time synchronization
Volume
Monitoring
Security
Images
Kernel fine-tuning
O&M
Troubleshooting
Remote log in issue
Linux operating system issue
Windows operating system issue
SSH log in issue
Operating system issue
veLinux operating system issue
Linux operating system issue
Windows operating system issue
Instance status issue
Instance unable to start issue
High instance load issue
GPU instances issue
Network connection issue
Network configuration issue
Storage classes issue
EBS Volume issue
Local Disk issue
Logs and monitoring issue
Third - party software issue
API Reference
Regions and availability zones
Instances
Images
HPC clusters
Key pairs
Tags
Volumes
Reserved storage capacity
Snapshot
Auto snapshot policy
Monitoring
Deployment sets
Launch templates
Cloud assistant
Patch management
SDK reference
CLI Reference
FAQ
Dedicated Host DDH
What's New
Billing
User Guide
Manage Dedicated Host
Manage Dedicated Host Cluster
Manage ECS instances
Monitoring and O&M
API reference
proprietary host
- Documentation
 Elastic Compute ServiceElastic Compute ServiceBest PracticesO&MUsing Ansible to install cloud assistant Agent
 Copy page
 Download PDF
O&M
Using Ansible to install cloud assistant Agent
Copy pageDownload PDFUsing Ansible to install cloud assistant Agent
This topic describes how to use the open-source tool Ansible to batch install cloud assistant Agent for Linux ECS instances.
What is Ansible
Ansible is an open-source tool for IT automation, which is developed based on Python. It is simple to use, secure, and reliable, with OpenSSH used for transmitting data (other transmission modes, such as the pull mode, are also supported). It is used to automatically configure, deploy applications, perform orchestration, and complete other remote tasks on managed nodes. For more details, see Ansible.
Terms
Term | Description |
Primary control node | Server with Ansible installed. It remotely logs in to and manages managed nodes via the SSH protocol. |
Managed node | The server to be managed by Ansible. In this practice, it refers to ECS instances on which cloud assistant Agent is to be installed. |
Usage notes
Nodes | Description |
Primary control node |
|
Managed node |
|
Procedure
- Install Ansible on the primary control node.
In the example provided in this practice, an ECS instance with the operating system CentOS 7.9 serves as the primary control node. To install Ansible on more operating systems, see Installation guide.
- Log in to the ECS instance serving as the primary control node. For more information, see Logging in to Linux instances.
- Execute the following command to install EPEL repository.
- yum install -y epel-release
- Execute the following command to install Ansible.
- yum install -y ansible
- Configure Ansible.
- Execute the following command to add EIPs of servers serving as managed nodes.
- vim /etc/ansible/hosts
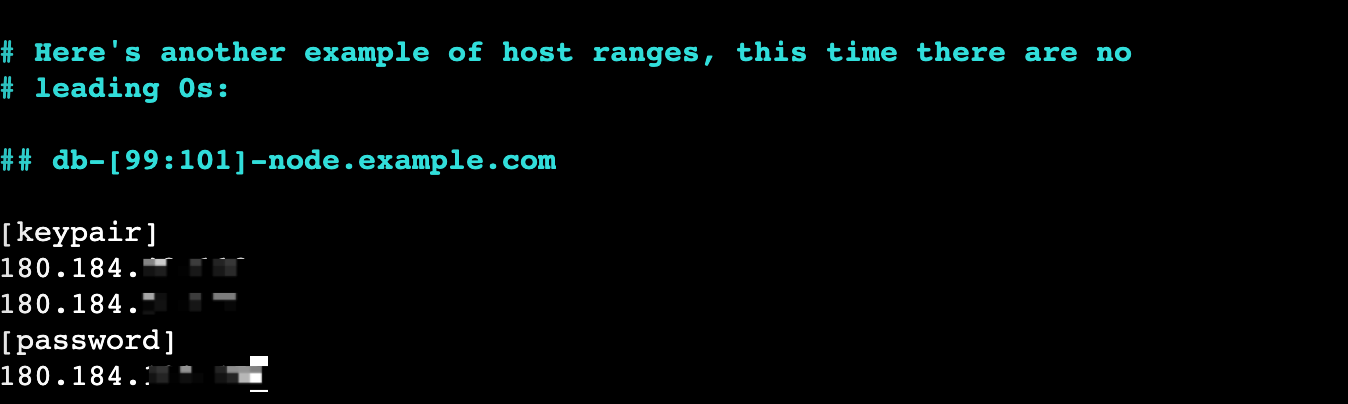
- Press the i key to add EIP addresses of managed nodes.
tip
You can also group different IP addresses in the format of [$groupname$] for easier batch operations by group. To learn more about Ansible grouping, see Inventory basics
- For example, instances can be divided into two groups: [keypair] (key pair-based login) and [password] (password-based login).
-
- Press esc and enter :wq to save the change and exit.
- Execute the following command to modify the Ansible configuration file.
- vim /etc/ansible/ansible.cfg
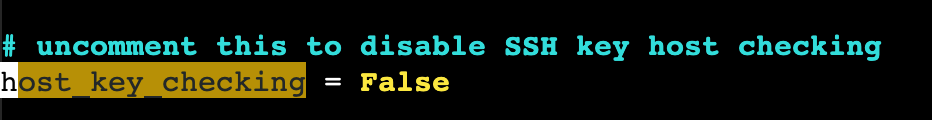
- Press the / key and enter host_key_checking to search for the keyword.
- At the beginning of the line containing host_key_checking = False, delete the # (comment character).
tip
After performing the above steps, you do not need to verify via SSH host key when logging in to managed nodes for the first time.
-
- Press esc and enter :wq to save the change and exit.
- (Optional) When logging in to a managed node by using a key pair, you can create a private key file for login.
- Execute the following command to create and edit the private key file.
In this practice, all managed nodes with key pair-based login use the same key pair.
- vim /root/key.pem
- Press the i key to paste the private key information into this file.
- Press esc and enter :wq to save the change and exit.
- Execute the following command to add read/write permissions on the private key file.
- chmod 600 /root/key.pem
- Install cloud assistant Agent on managed nodes.
tip
In the example provided in this practice, after cloud assistant Agent is installed, restarting managed nodes is not required.
- On the ECS instance serving as the primary control node, execute the following command to install Agent for ECS instances with key pair-based login grouped in [keypair].
tip
- Replace keypair with actual group name.
- Replace ~/key.pem with actual path where the login key for managed nodes is stored.
- sudo ansible -i /etc/ansible/hosts keypair -b --become-user=root -m shell -a 'sudo bash -c "$(curl https://assist-client.tos-cn-beijing.volces.com/install.sh)"' --private-key=~/key.pem
- You can view the installation progress and results for each instance based on script responses.
-

- On the ECS instance serving as the primary control node, execute the following command and enter the login password of the managed node. This enables you to install Agent for the instance with password-based login grouped in [password].
tip
Replace password with the actual group name.
- sudo ansible -i /etc/ansible/hosts password -b --become-user=root -m shell -a 'sudo bash -c "$(curl https://assist-client.tos-cn-beijing.volces.com/install.sh)"' -k
-

- Check the running status of cloud assistant Agent on each managed node.
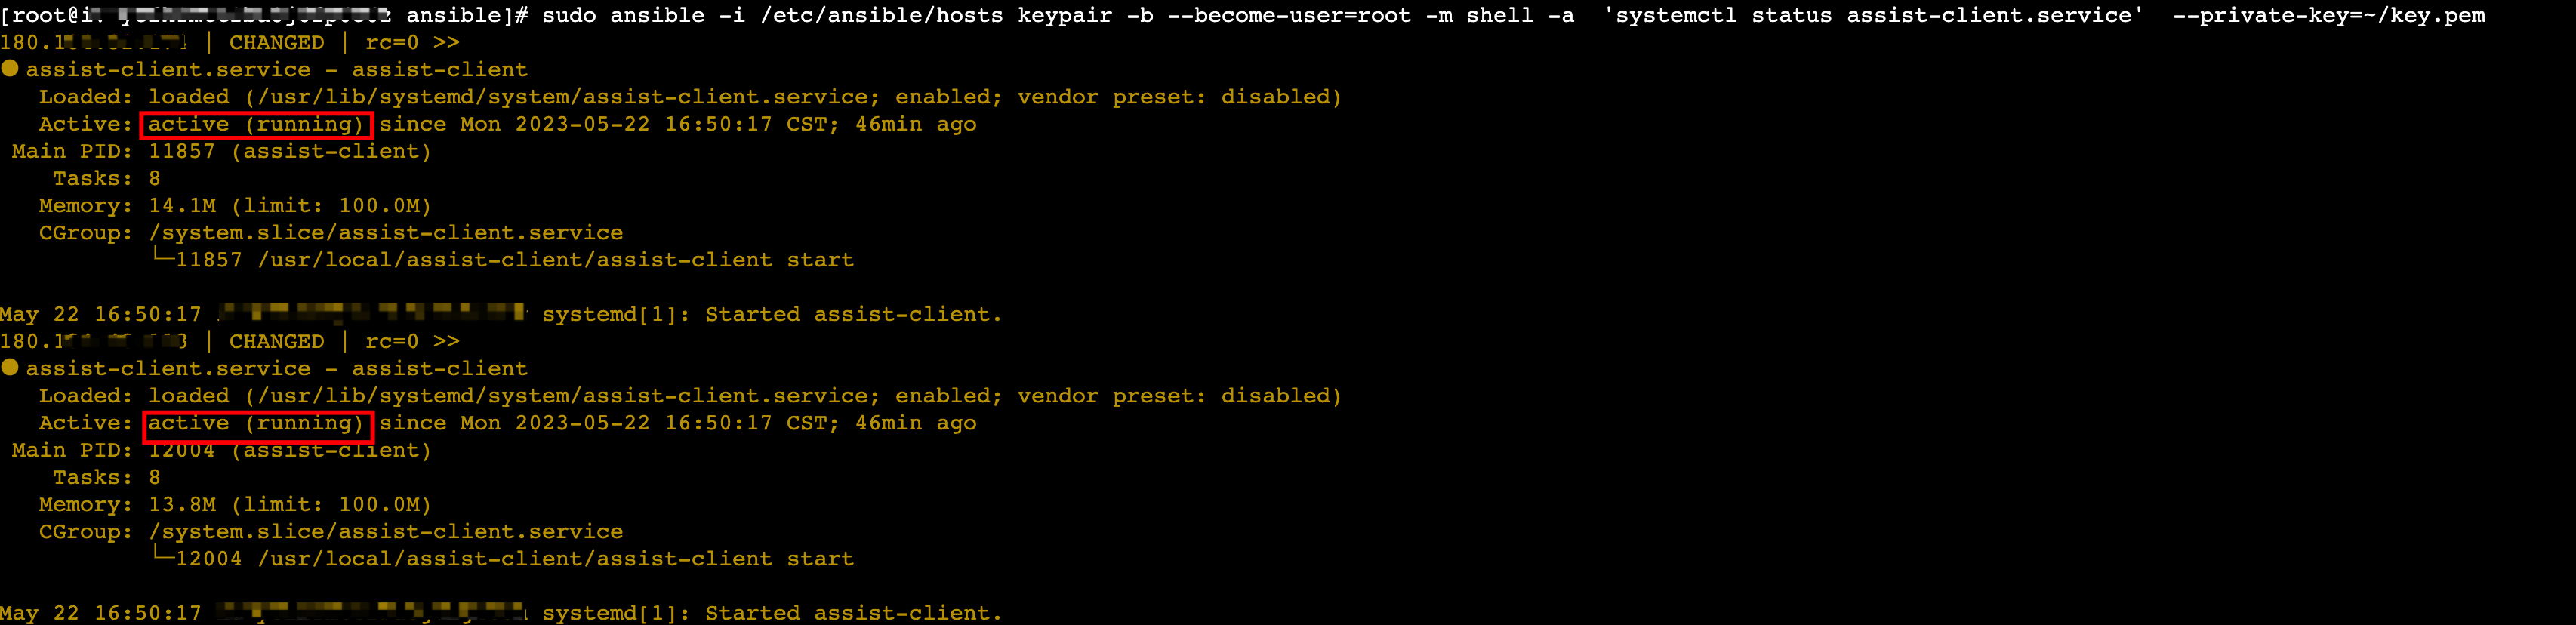
- Execute the following command to view the Agent status on ECS instances with key pair-based login and grouped in [keypair].
- sudo ansible -i /etc/ansible/hosts keypair -b --become-user=root -m shell -a 'systemctl status assist-client.service' --private-key=~/key.pem
- Sample instance in a normal status:
-
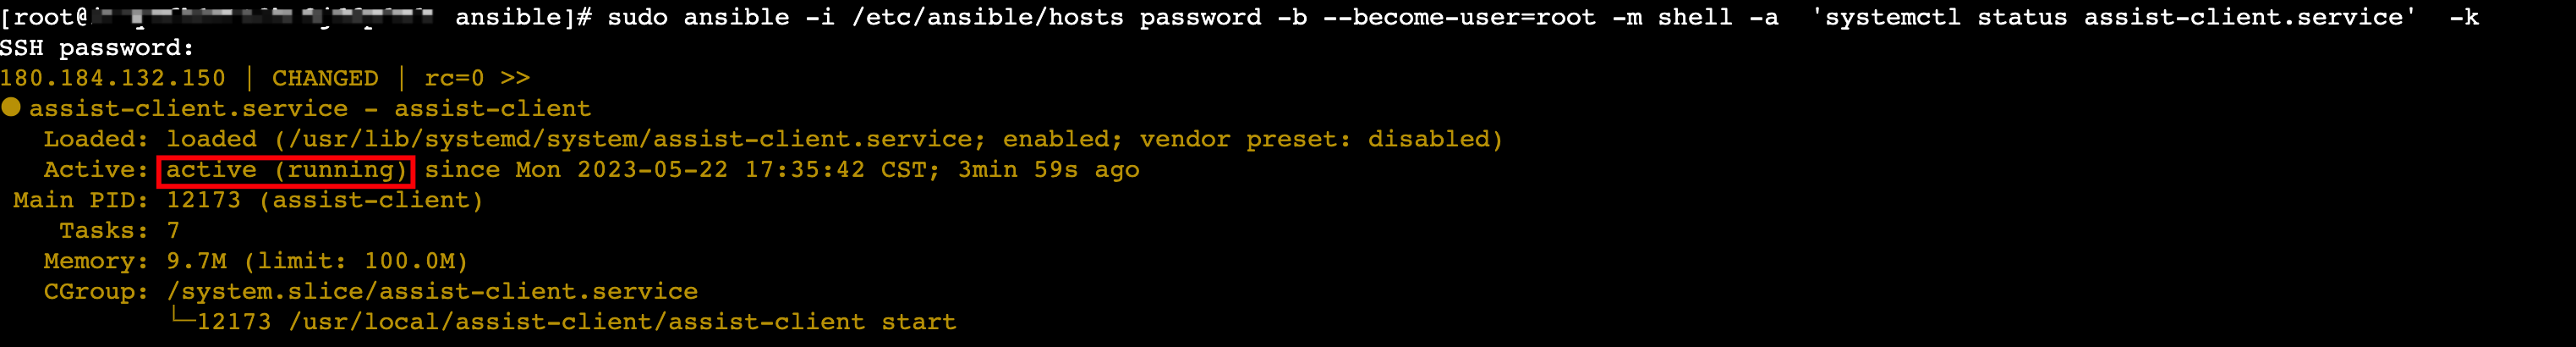
- To view the Agent status on the ECS instance with password-based login grouped in [password], execute the following command and then enter the login password of the managed node.
- sudo ansible -i /etc/ansible/hosts password -b --become-user=root -m shell -a 'systemctl status assist-client.service' -k
- Sample instance in a normal status:
-
Last updated: 2025.11.05 10:29:11
All rights reserved © Beijing Volcano Engine Technology Co., Ltd2024
