Volcengine Managed Service for Prometheus
Volcengine Managed Service for Prometheus


Document

- Documentation
 Volcengine Managed Service for PrometheusBest practicesAccessing workspaces across clouds and across regionsAchieving cross-region access to workspaces by using CEN and PrivateLink
 Copy page
 Download PDF
Accessing workspaces across clouds and across regions
Achieving cross-region access to workspaces by using CEN and PrivateLink
Copy pageDownload PDFAchieving cross-region access to workspaces by using CEN and PrivateLink
The workspace of Volcengine Managed Service for Prometheus (VMP) can be accessed over the Internet through PrivateLink. This topic describes how to configure PrivateLink to read and write data in a VMP workspace.
tip
We recommend that you use a Volcano Engine root user to configure and use this feature. If you use an Identity and Access Management (IAM) user to create an endpoint, you may not be able to select an available endpoint service. For more details, see Why can't I select an available endpoint service when creating an endpoint?
Background
A VMP workspace offers a standard remote write URL and a standard query URL that can be accessed over internal networks. This allows you to collect service metrics and business metrics in the internal networks of the public cloud and deploy Grafana in a Volcengine Kubernetes Engine (VKE) cluster to create and view metric dashboards. For more details, see Deploying Grafana and connecting to a workspace in the VKE cluster.
In some scenarios, you may need to establish connections between different regions of Volcano Engine to write or query data from the same Prometheus workspace in different regions. In this case, you can achieve cross-region access to VMP workspaces by using Cloud Enterprise Network (CEN) and PrivateLink.
tip
- For more information about PrivateLink, refer to What is PrivateLink?
- For more information about CEN, refer to What is Cloud Enterprise Network?
Prerequisites
- A VMP workspace has been created, and basic authentication has been enabled. For details, see Creating workspaces.
- A virtual private cloud (VPC) is created in each region.
Procedure
tip
This topic provides an example of how to configure the query URL of a VMP workspace by using PrivateLink. This configuration method applies to other addresses.
Step 1: Configure CEN
- Log in to the CEN console.
- In the left navigation pane, click CEN Instances. On the page that appears, click Create CEN to create a CEN instance.
- Click the name of the created CEN instance to go to the instance details page.
- Click the Network Instances tab and click Install Network Instances to add two VPC instances in different regions.
-
- Click the Inter-region bandwidth tab and click Associate BWP to create and bind a bandwidth package between two regions. Then, click Allocate Inter-region bandwidth to allocate cross-region bandwidth, thereby connecting networks across different regions.
tip
Step 2: Configure an endpoint
Create an endpoint in the region where the VMP workspace is located. This topic takes the China (Shanghai) region as an example. Procedure:
- Log in to the VPC console.
- In the left navigation pane, click PrivateLink > Endpoint, and click the Interface Endpoint tab. Click Create Endpoint.
- Specify the information about the endpoint.
- Basic information: Select the region where the VMP workspace is deployed, specify the endpoint name, and select Interface for the Type parameter.
- Endpoint Service: Select VolcanoEngine Services for the Add method parameter, and select the service that corresponds to VMP for the Endpoint Service parameter. You can select one of the following services:
- VMP read-only service: This service is used to query data of the VMP workspace.
- VMP write-only service: This service is used to write data in the VMP workspace.
- Network configuration: Select the user VPC, availability zone, subnet, and security group.
tip
- For more details about the configuration of the endpoint, see Creating interface endpoints.
- Make sure that the security group allows traffic on port 8080. Otherwise, the port may be inaccessible.
- In the read/write splitting scenarios, you need to separately create endpoints for reading and writing and use different domain names for the endpoints.
- Click Buy now and check again to complete the configuration.
Step 3: Check the endpoint connection status
- After VMP automatically accepts the endpoint connection request, the network connection status of the endpoint changes to Connected, which indicates that the connection is successful. In this case, you can access VMP by using the domain name of the endpoint.
- (Optional) In an Elastic Compute Service (ECS) instance or a pod in the VPC bound to the endpoint, run the following command to access the endpoint domain name and check whether the endpoint, domain name, and network are working as expected.
-
- The following section shows the expected result: If a response is returned when you access the endpoint domain name, the connection is normal and the network is connected.
-
-
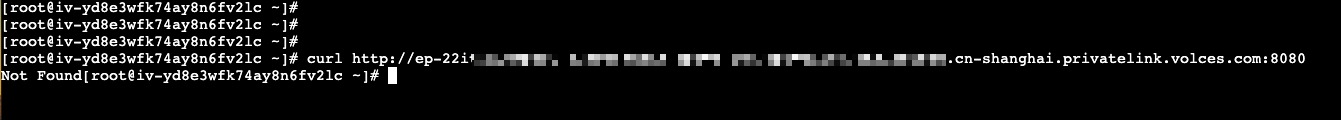
Validate results
After the network is connected, you can access the VMP workspace across regions to read data from and write data to the workspace. The following section provides an example of how to deploy Grafana in a cluster in the China (Beijing) region to access the VMP workspace in the China (Shanghai) region.
- Deploy Grafana in a VKE cluster in China (Beijing). For more details, see Deploying Grafana and connecting to a workspace in the VKE cluster.
- Run the following command to configure Grafana port forwarding:
-
- Open a browser in your local environment (Linux/Mac), paste localhost:3000 into the address bar, and then press Enter to go to the Grafana login page. Log in to Grafana by using the default username admin and password admin.
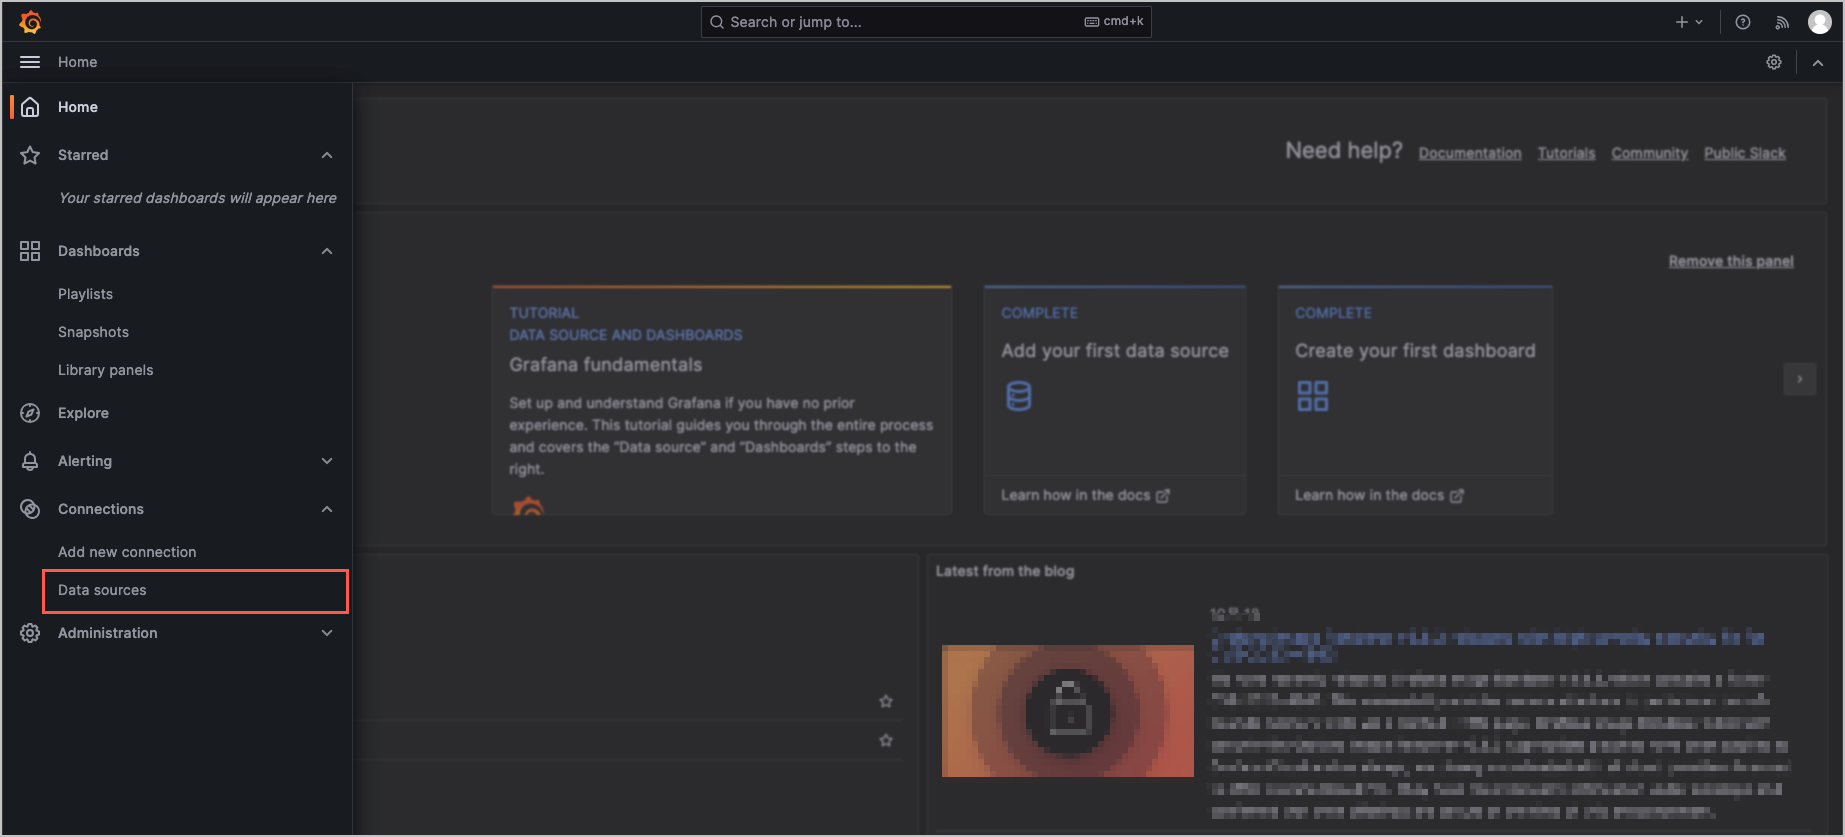
- Click Connections > Data sources in the left navigation pane.
-
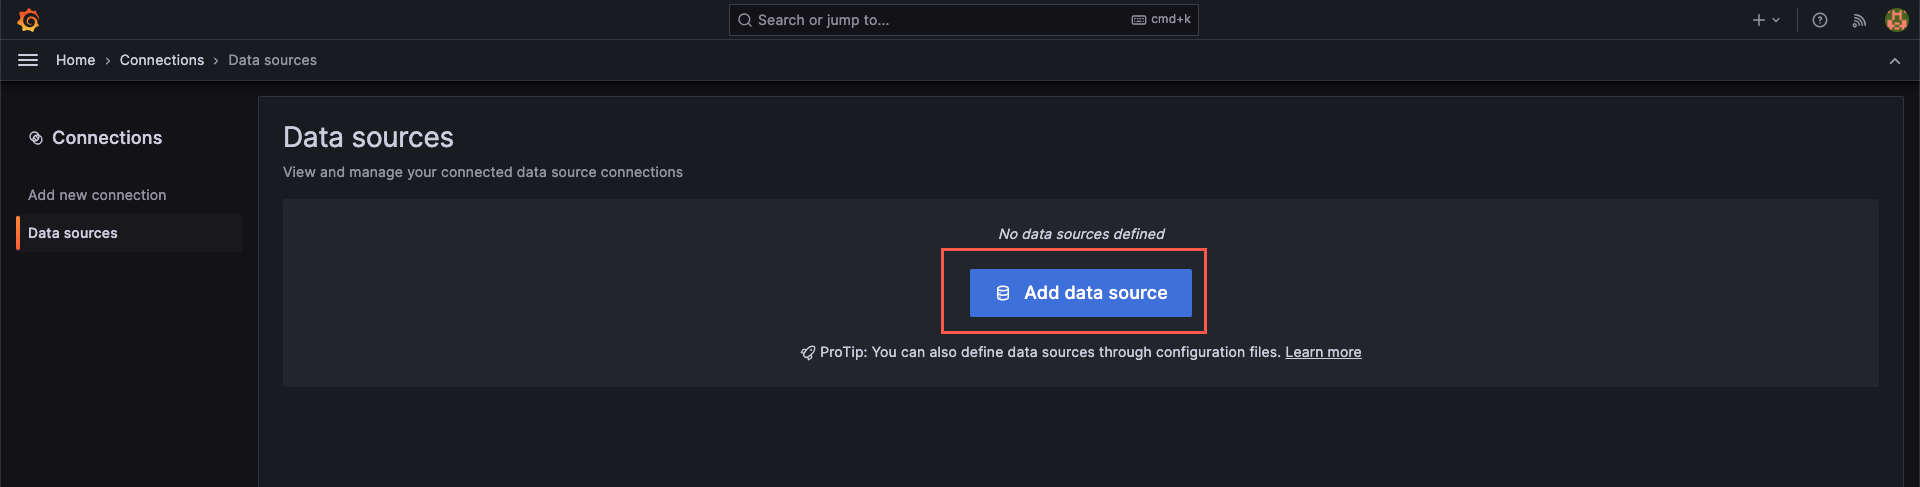
- Click Add data source to create a new data source.
-
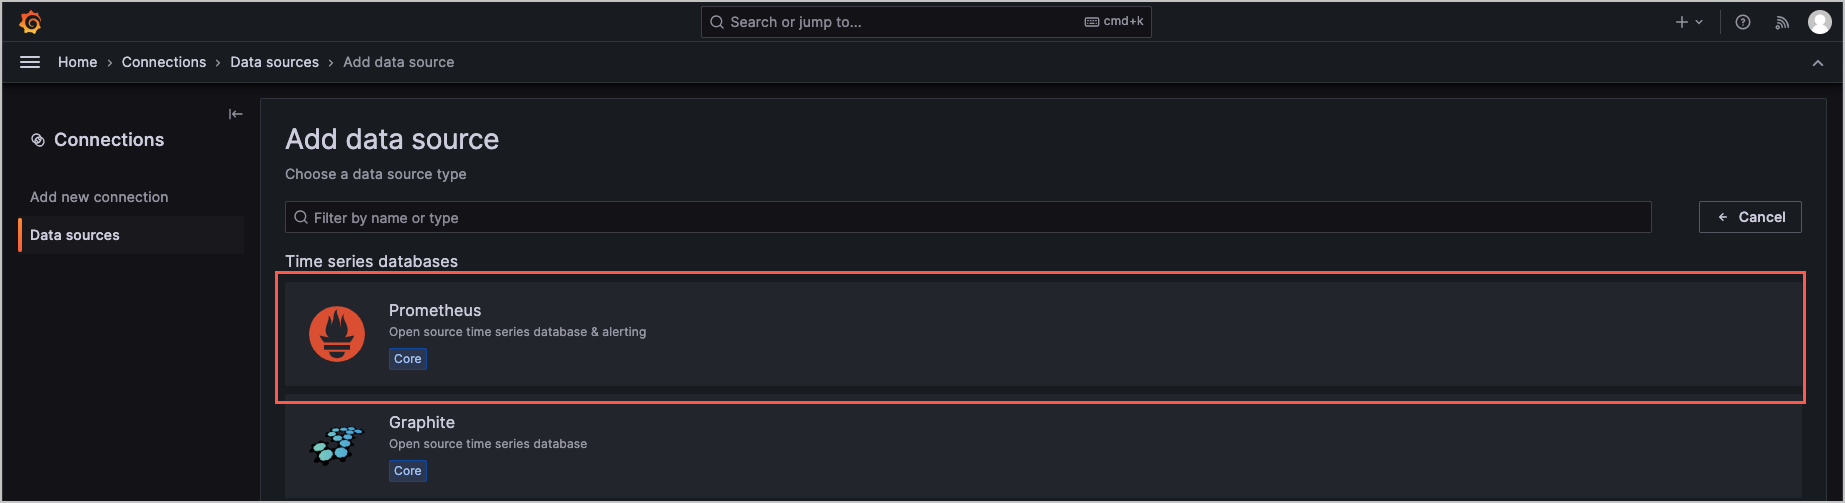
- On the Add data source page, click Prometheus.
-
- In the HTTP section, paste the modified query URL of the workspace in the Prometheus server URL field.
tip
You need to modify the original query URL of the workspace as follows:
- Change the domain name to the domain name of the endpoint.
- Add port 8080 next to the domain name.
- The values of other parameters remain unchanged.
For example, change the query URL of the workspace to http://ep-5gs***.epsvc-22j124***.cn-shanghai.privatelink.volces.com:8080/workspaces/b73***.
-
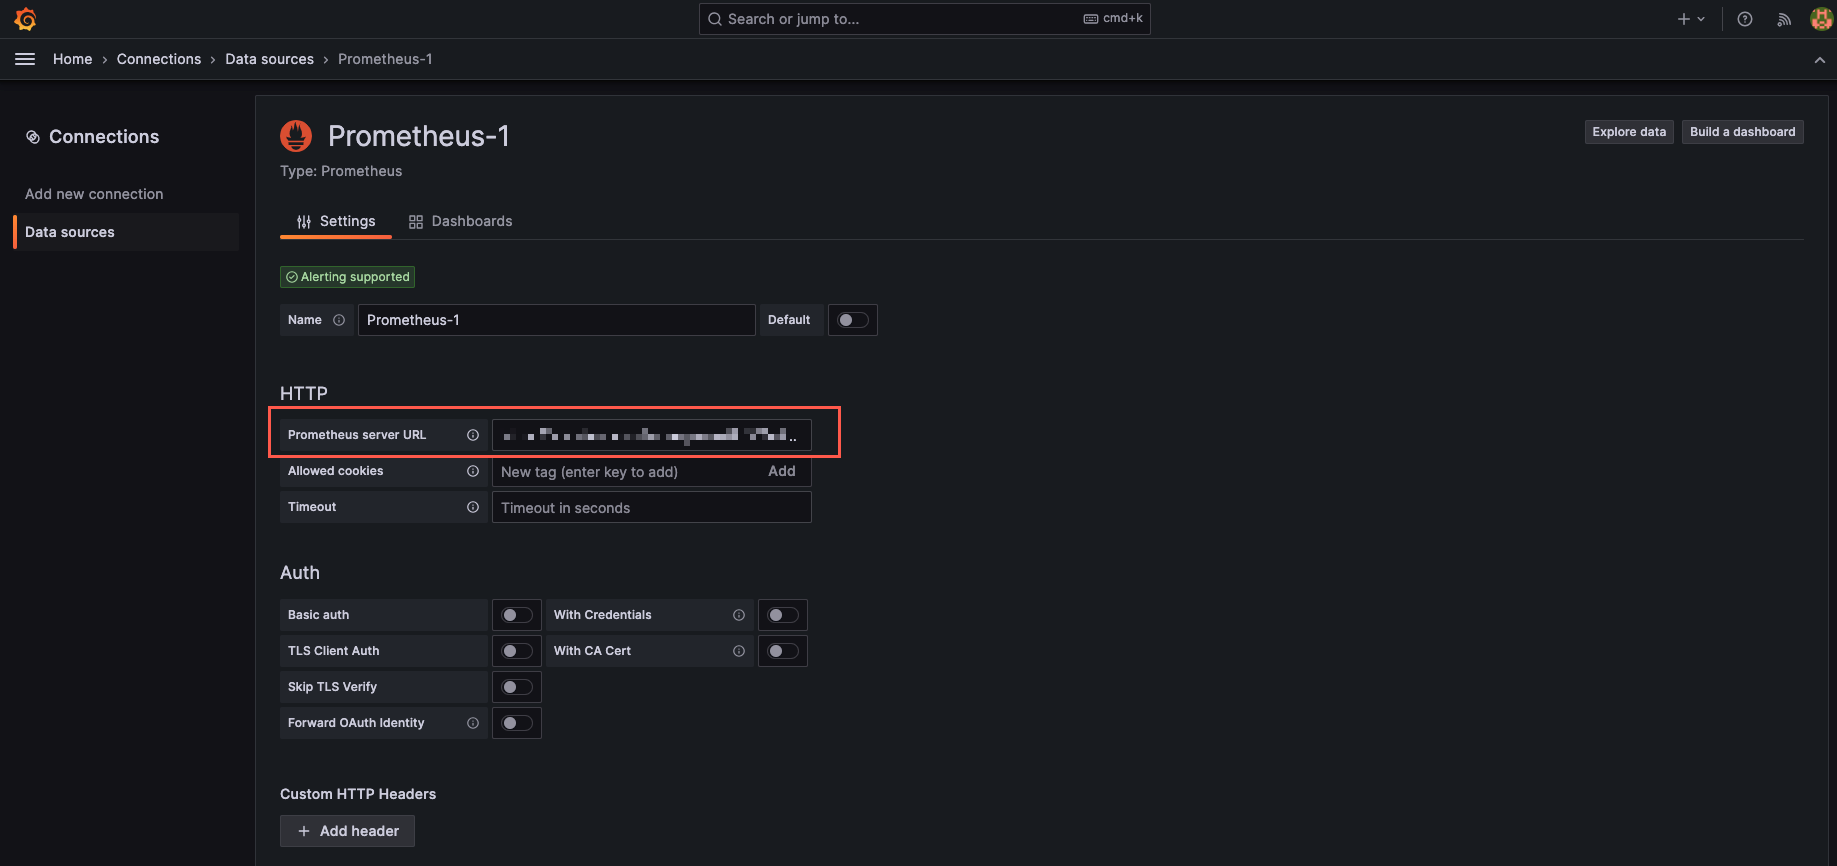
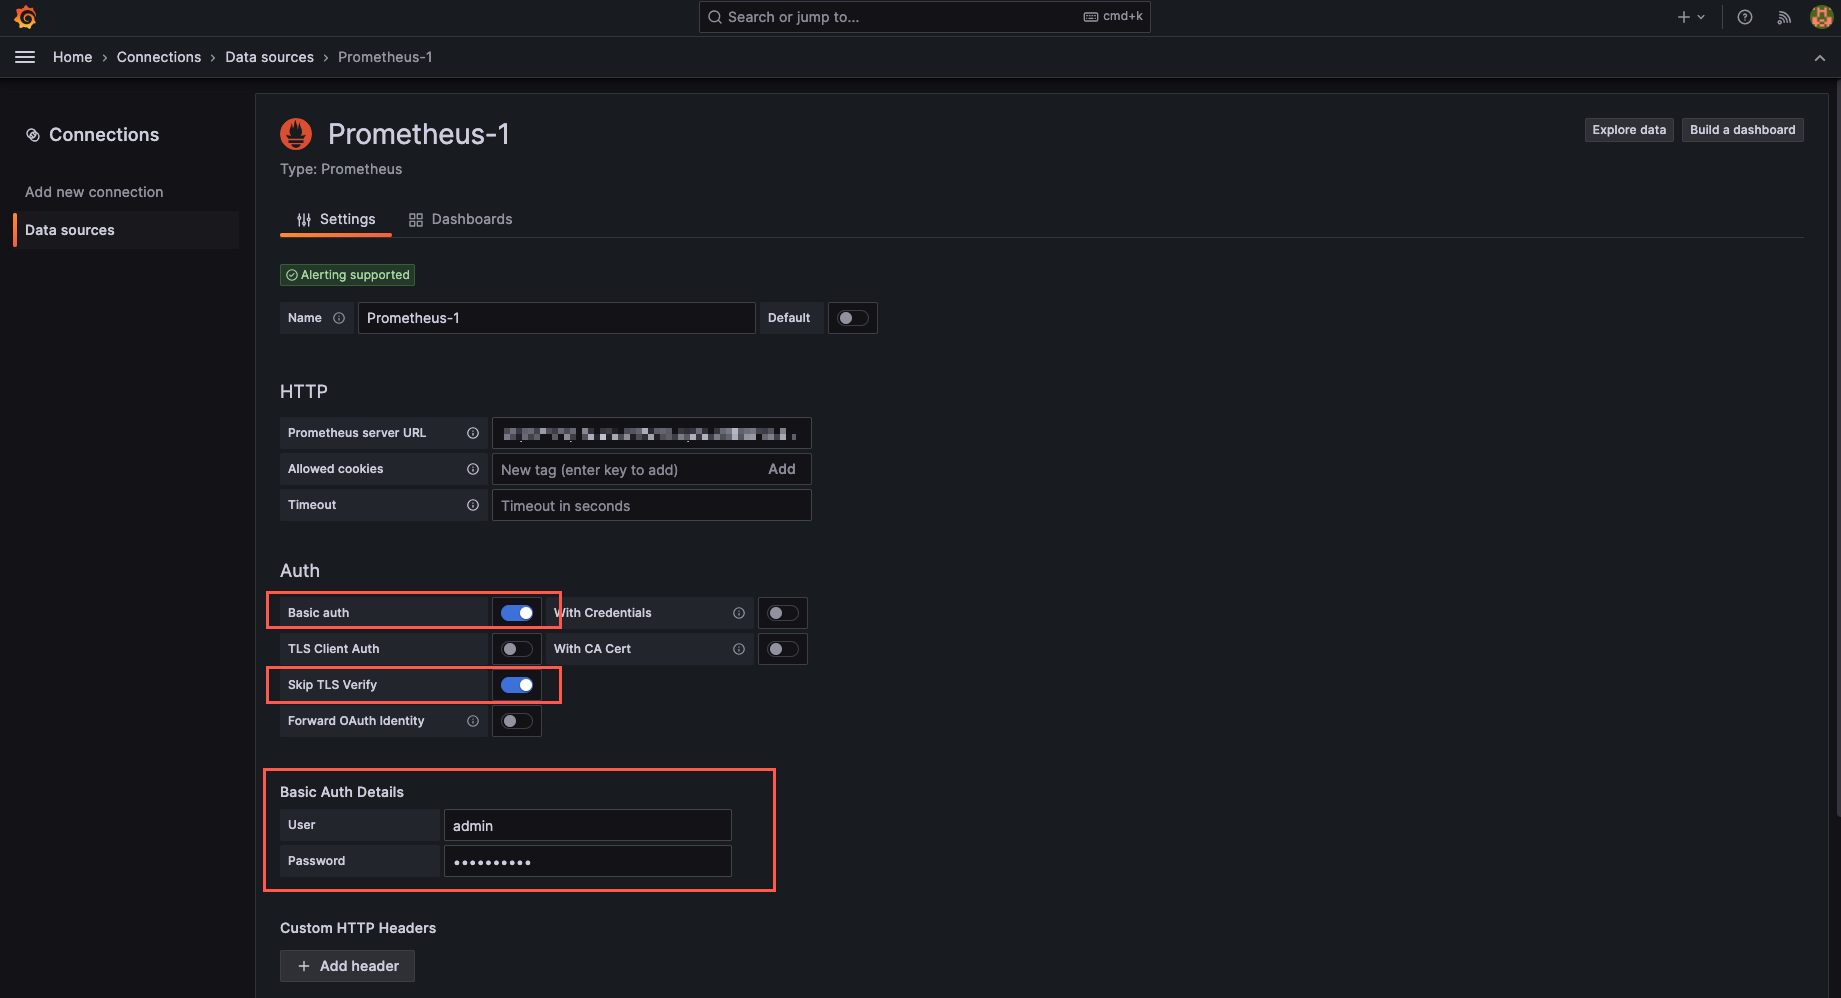
- Switch on Basic auth in the Auth section and configure the username and password used for workspace authentication in the Basic Auth Details section.
-
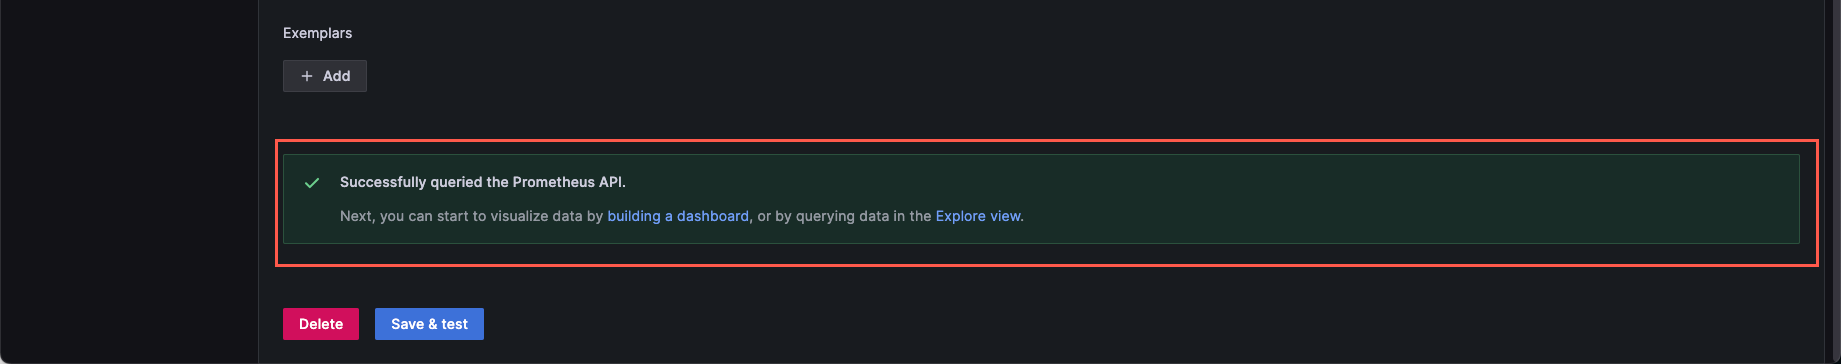
- Click Save & test at the bottom of the page. When the message Successfully queried the Prometheus API is displayed, it indicates the data source is configured and the workspace is integrated with Grafana.
-
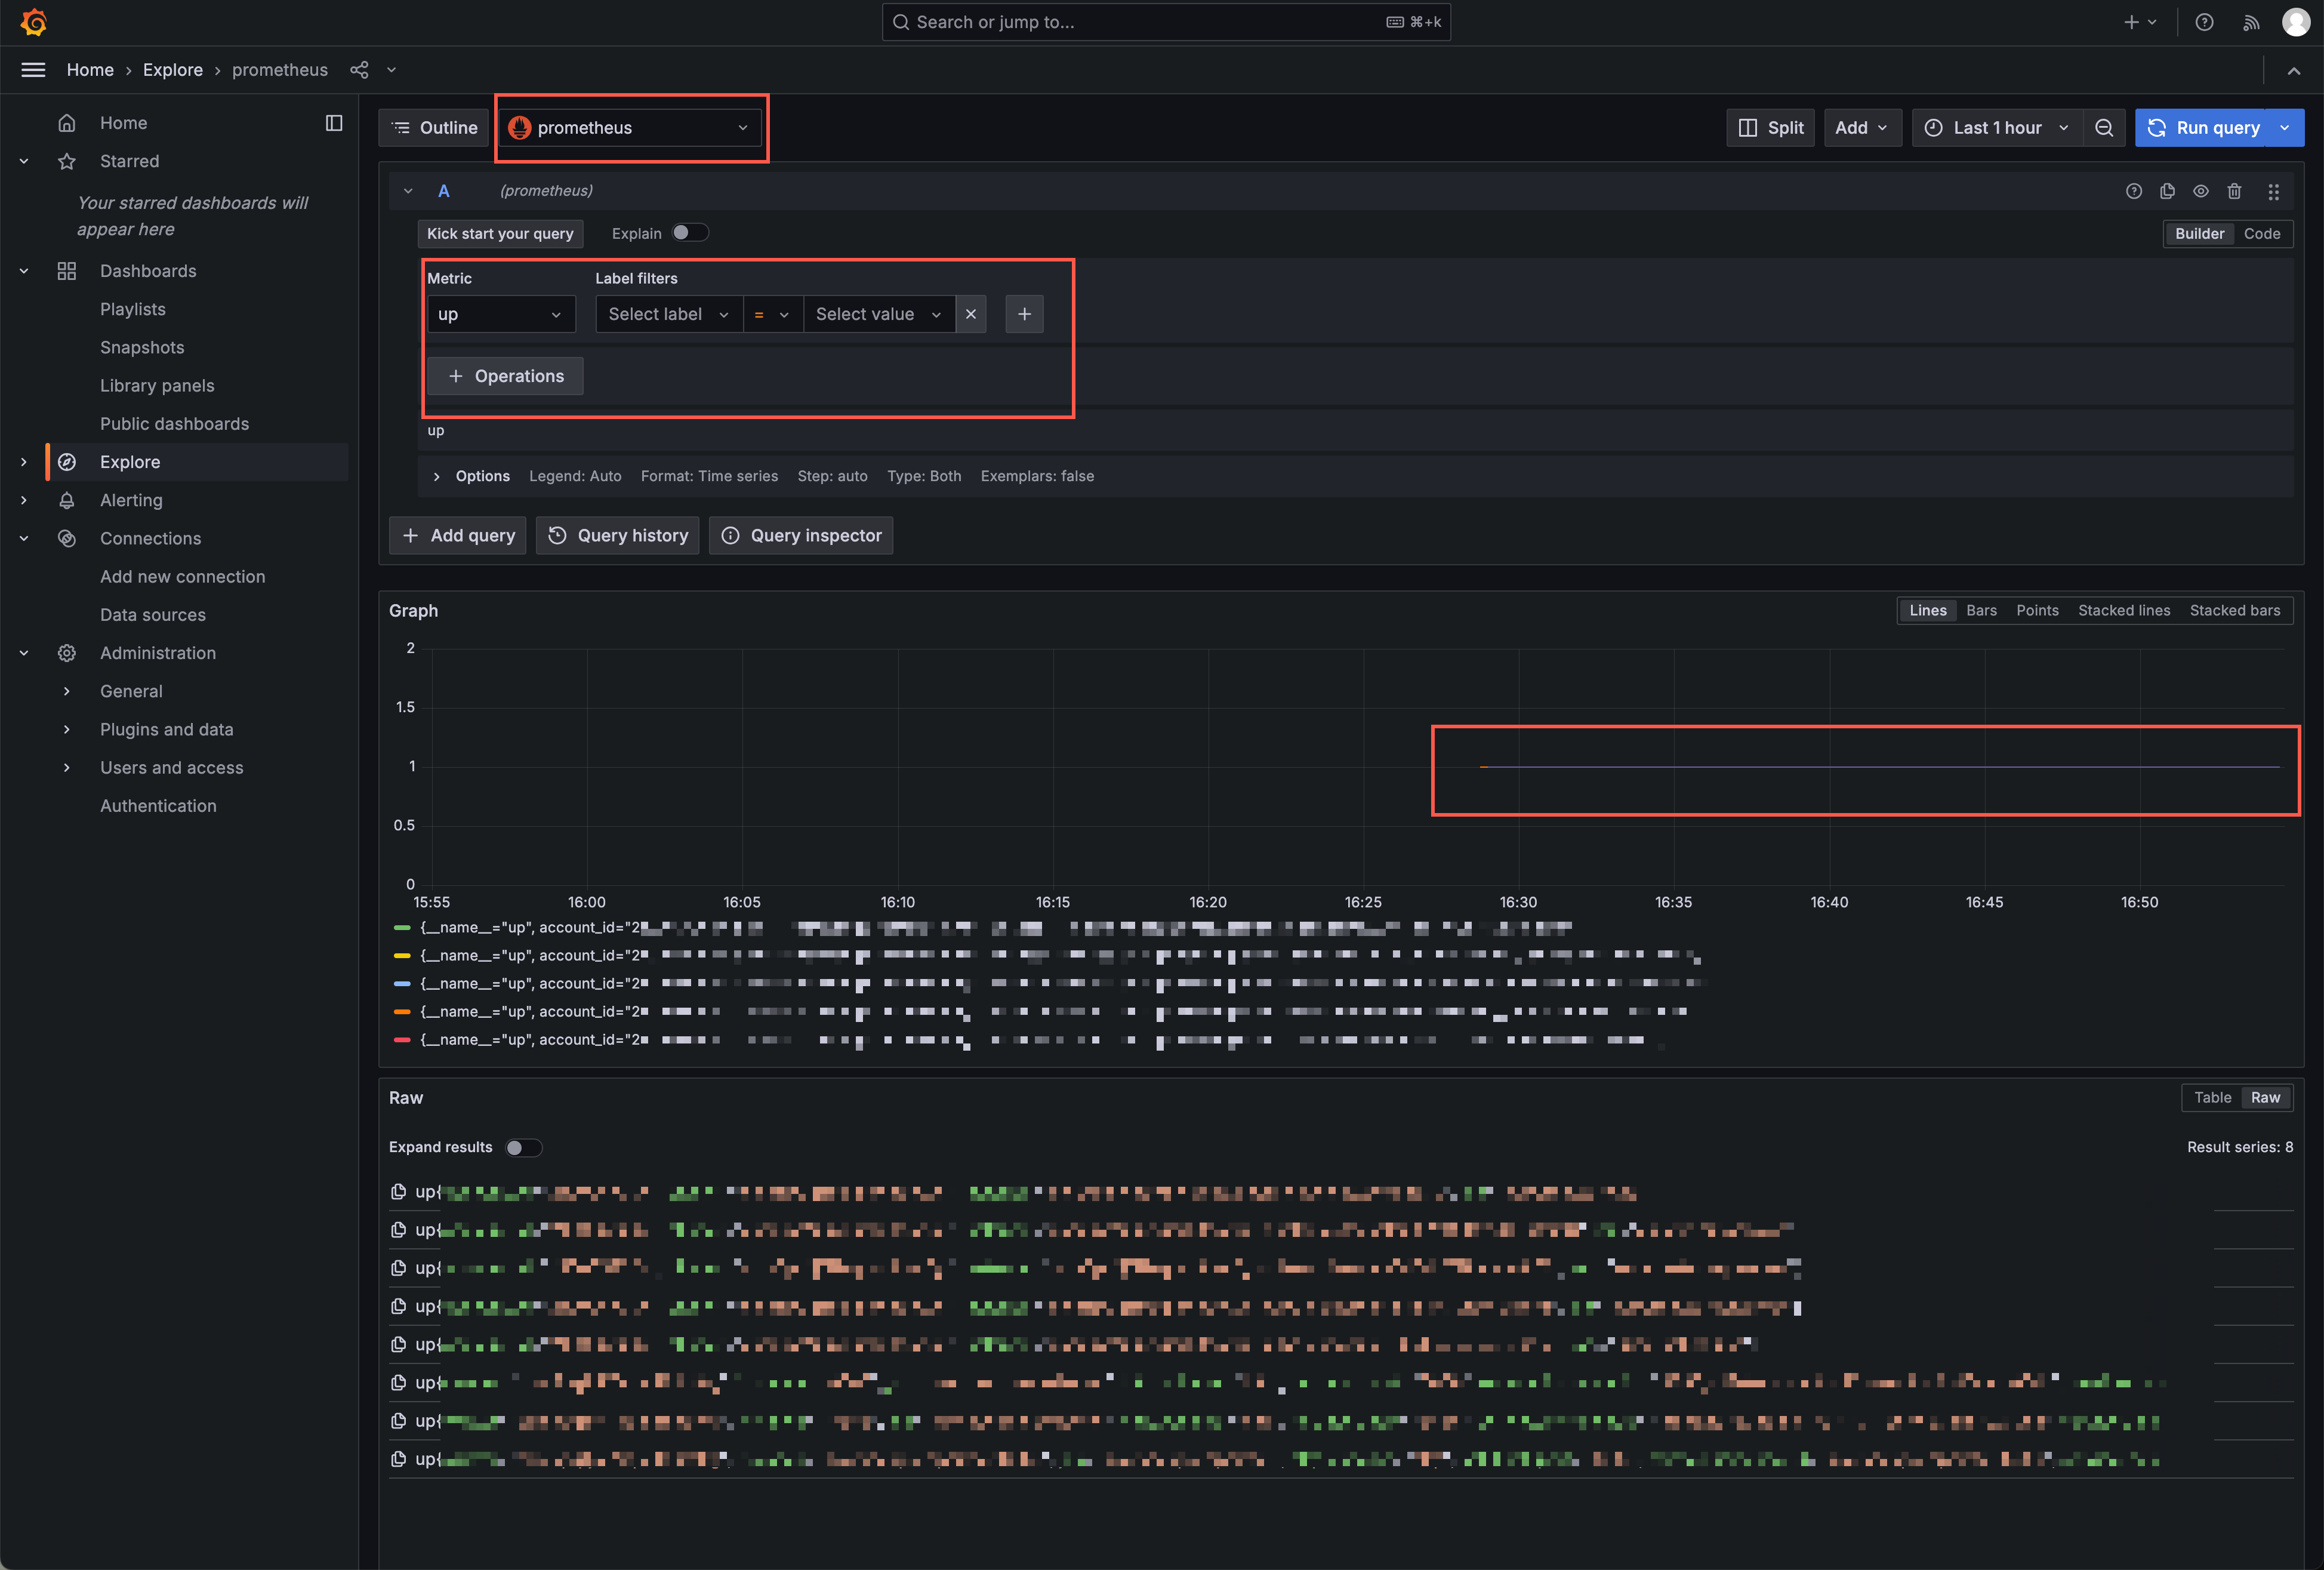
- Click Explore in the left navigation pane of the Grafana platform. Then, you can query the data in the workspace as expected.
-
Monitoring and O&M
After you achieve cross-region access to the workspace by using CEN and PrivateLink, you can view the details and monitoring information of the CEN instance and the endpoint.
For more configuration details, refer to the official documentation of CEN and the official documentation of PrivateLink.
Last updated: 2026.10.10 11:04:51
All rights reserved © Beijing Volcano Engine Technology Co., Ltd2024
