Volcengine Managed Service for Prometheus
Volcengine Managed Service for Prometheus


Document

- Documentation
 Volcengine Managed Service for PrometheusBest practicesResource and application monitoringMonitoring ECS instances by using node-exporter
 Copy page
 Download PDF
Resource and application monitoring
Monitoring ECS instances by using node-exporter
Copy pageDownload PDFMonitoring ECS instances by using node-exporter
Volcengine Managed Service for Prometheus (VMP) allows you to monitor Elastic Compute Service (ECS) instances to obtain the metric information of the ECS instances. This topic describes how to monitor ECS instances by using node-exporter.
Background
node-exporter is an important component in the Prometheus open-source ecosystem. It collects metrics from Linux server hardware and operating systems, such as CPU, memory, disk, network, and file systems. It provides the metric data as an HTTP service to help Prometheus scrape the data and thus monitor the operational status of Linux servers.
Compared with other monitoring tools, node-exporter mainly provides the following benefits:
- Deep integration with the Prometheus ecosystem: As an official Prometheus component, node-exporter works seamlessly with Alertmanager and Grafana to form a complete monitoring loop.
- Lightweight and efficient: Developed in the Go language, node-exporter occupies few resources, has a minimal impact on monitored node performance, and applies to large-scale cluster deployment.
- Comprehensive and flexible metric collection: By default, node-exporter covers system underlying metrics and allows you to add custom metrics by using custom scripts or add-ons such as the text file collector. This enables node-exporter to apply to different monitoring scenarios.
- Active community and rich ecosystem: Leveraging the large Prometheus community, node-exporter is updated and maintained in a timely manner, supports node auto-discovery in cloud-native environments such as Kubernetes, and adapts to the containerized deployment trend.
Prerequisites
- VMP and ECS must be deployed in the same region.
- An ECS instance is created and bound to a public IP address. For more details, refer to Using the wizard to buy ECS instances.
- A VMP workspace has been created. For details, see Creating workspaces.
Procedure
Step One: Configure a security group
- Log in to the VPC console.
- Click Security Group in the left navigation pane.
- Click Create Security Group in the security group list and configure the security group for the hosted collector. The security group will be bound to the Elastic Network Interface (ENI) of the pod for the hosted collector during the configuration of an integration task, which allows the hosted collector to access the specified target IP address ranges and ports.
- Click the VPC drop-down menu and select the VPC of the user.
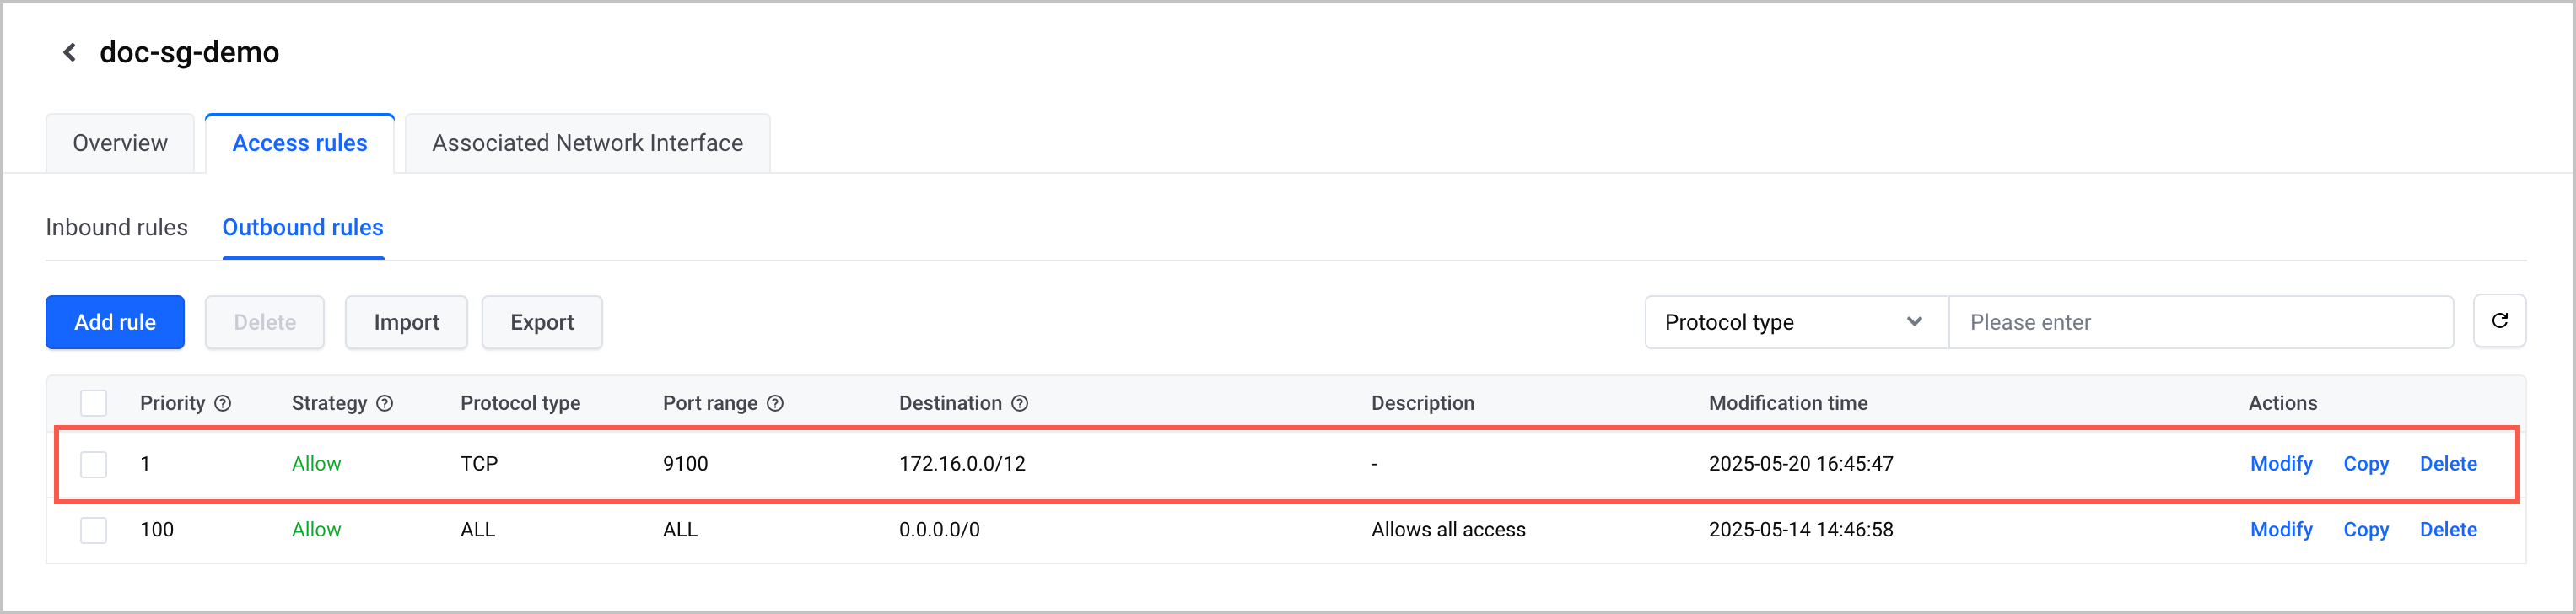
- In the Access Rules section, click the Outbound tab and click Add Rule. Then, configure the security rules for the hosted collector. Set the Destination parameter to the CIDR block where the collection target is located, such as 172.16.0.0/12, set the Protocol type parameter to TCP, and set the Port range parameter to 9100.
-
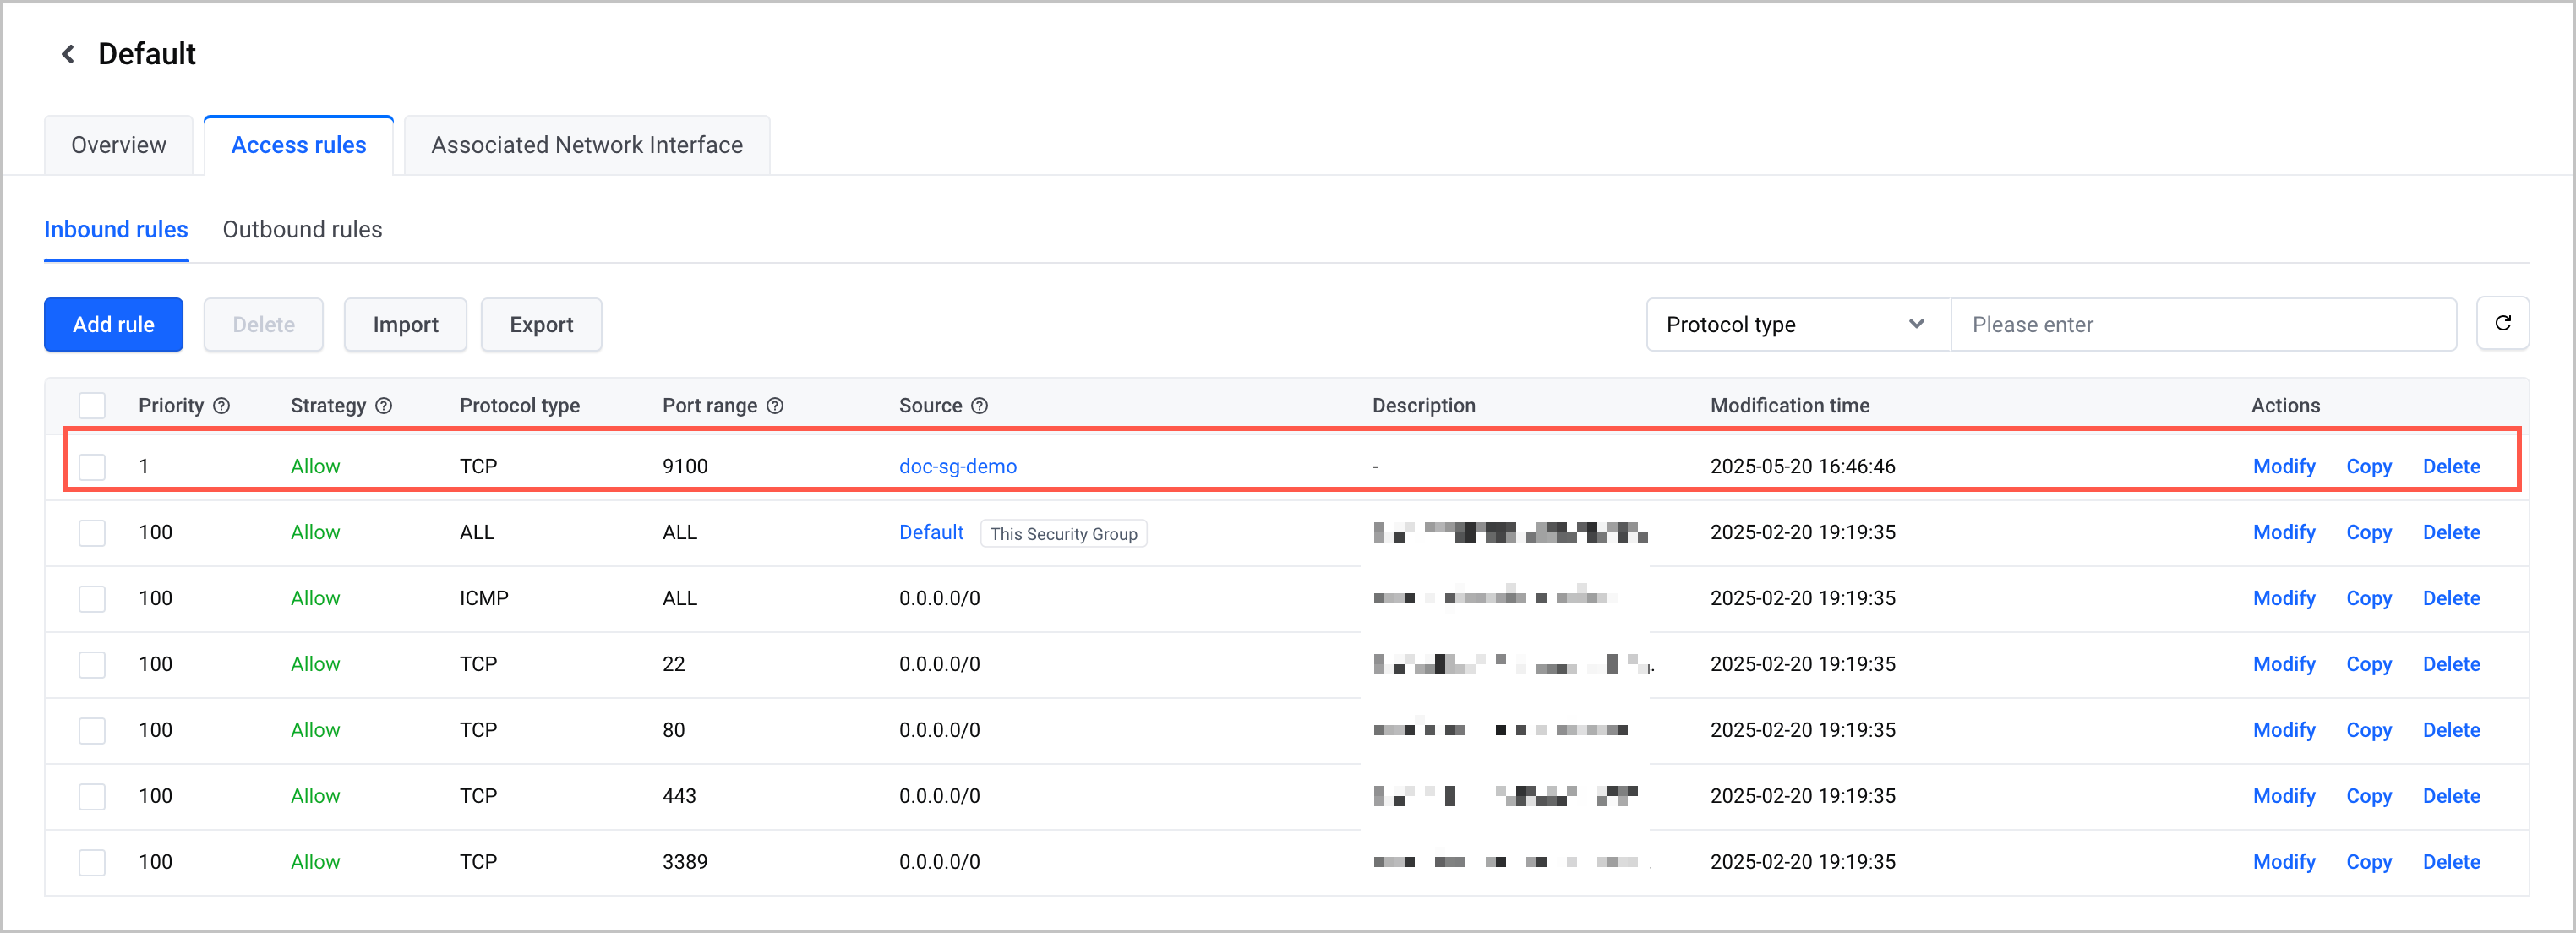
- Configure the security group used by the ECS instance. This topic uses the Default security group as an example. On the Inbound Rules tab, click Add Rule to add a rule to allow traffic on the metric collection port. Set the Source parameter to the security group configured for the collector, set the Protocol type parameter to TCP, and set the Port range parameter to 9100.
-
tip
You can also create a new security group and add both the hosted collector and the ECS instance to the new security group. In this case, you do not need to configure new access rules. The default outbound and inbound rules in the new security group allow mutual access between the hosted collector and the ECS instance.
Step 2: Deploy node-exporter in the ECS instance
- Log in to the ECS console.
- Click Instance & Image > Instance in the left navigation bar to go to the instance list page. Click the name of the target instance to go to the instance details page.
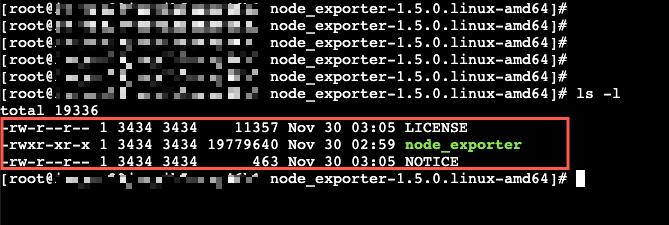
- Run the following command to download and decompress the file package of node-exporter:
tip
If you cannot download the exporter on the ECS instance, you can download the package to your local host and upload it to ECS. For more details, refer to Using SCP to upload files from a local Linux or MacOS to a Linux instance.
- Go to the decompressed folder and run the following command to start node-exporter:
- Run the following command to view the metrics exposed by node-exporter and check whether it is running as expected:
The following section shows the expected response result, in which the collected metrics can be viewed.
Step 3: Configure an integration task
- Log in to the VMP console. the
- In the top navigation bar, select the target region.
- Click Access Center > Component in the left navigation pane.
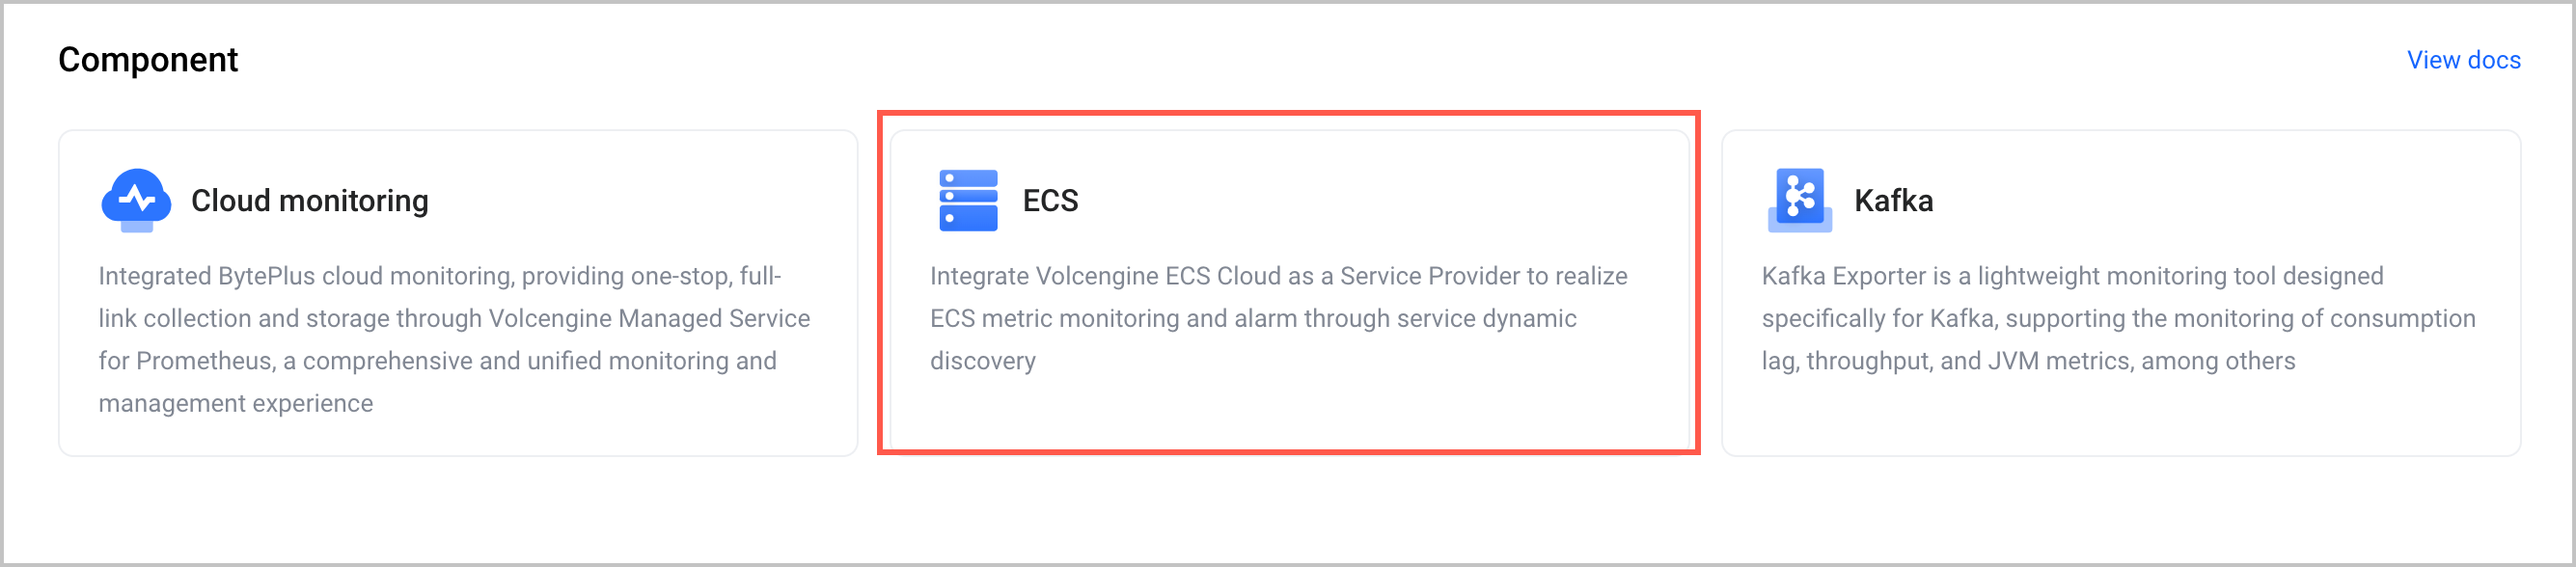
- Click ECS to configure the ECS integration task.
-
- (Optional) Service authorization.
- When you configure an ECS integration task for the first time, you need to grant permissions to allow VMP to access ECS and VPC. Click Authorize to configure service authorization.
- Click Authorize Now to authorize VMP to access other services.
- Configure the details of the integration task.
-
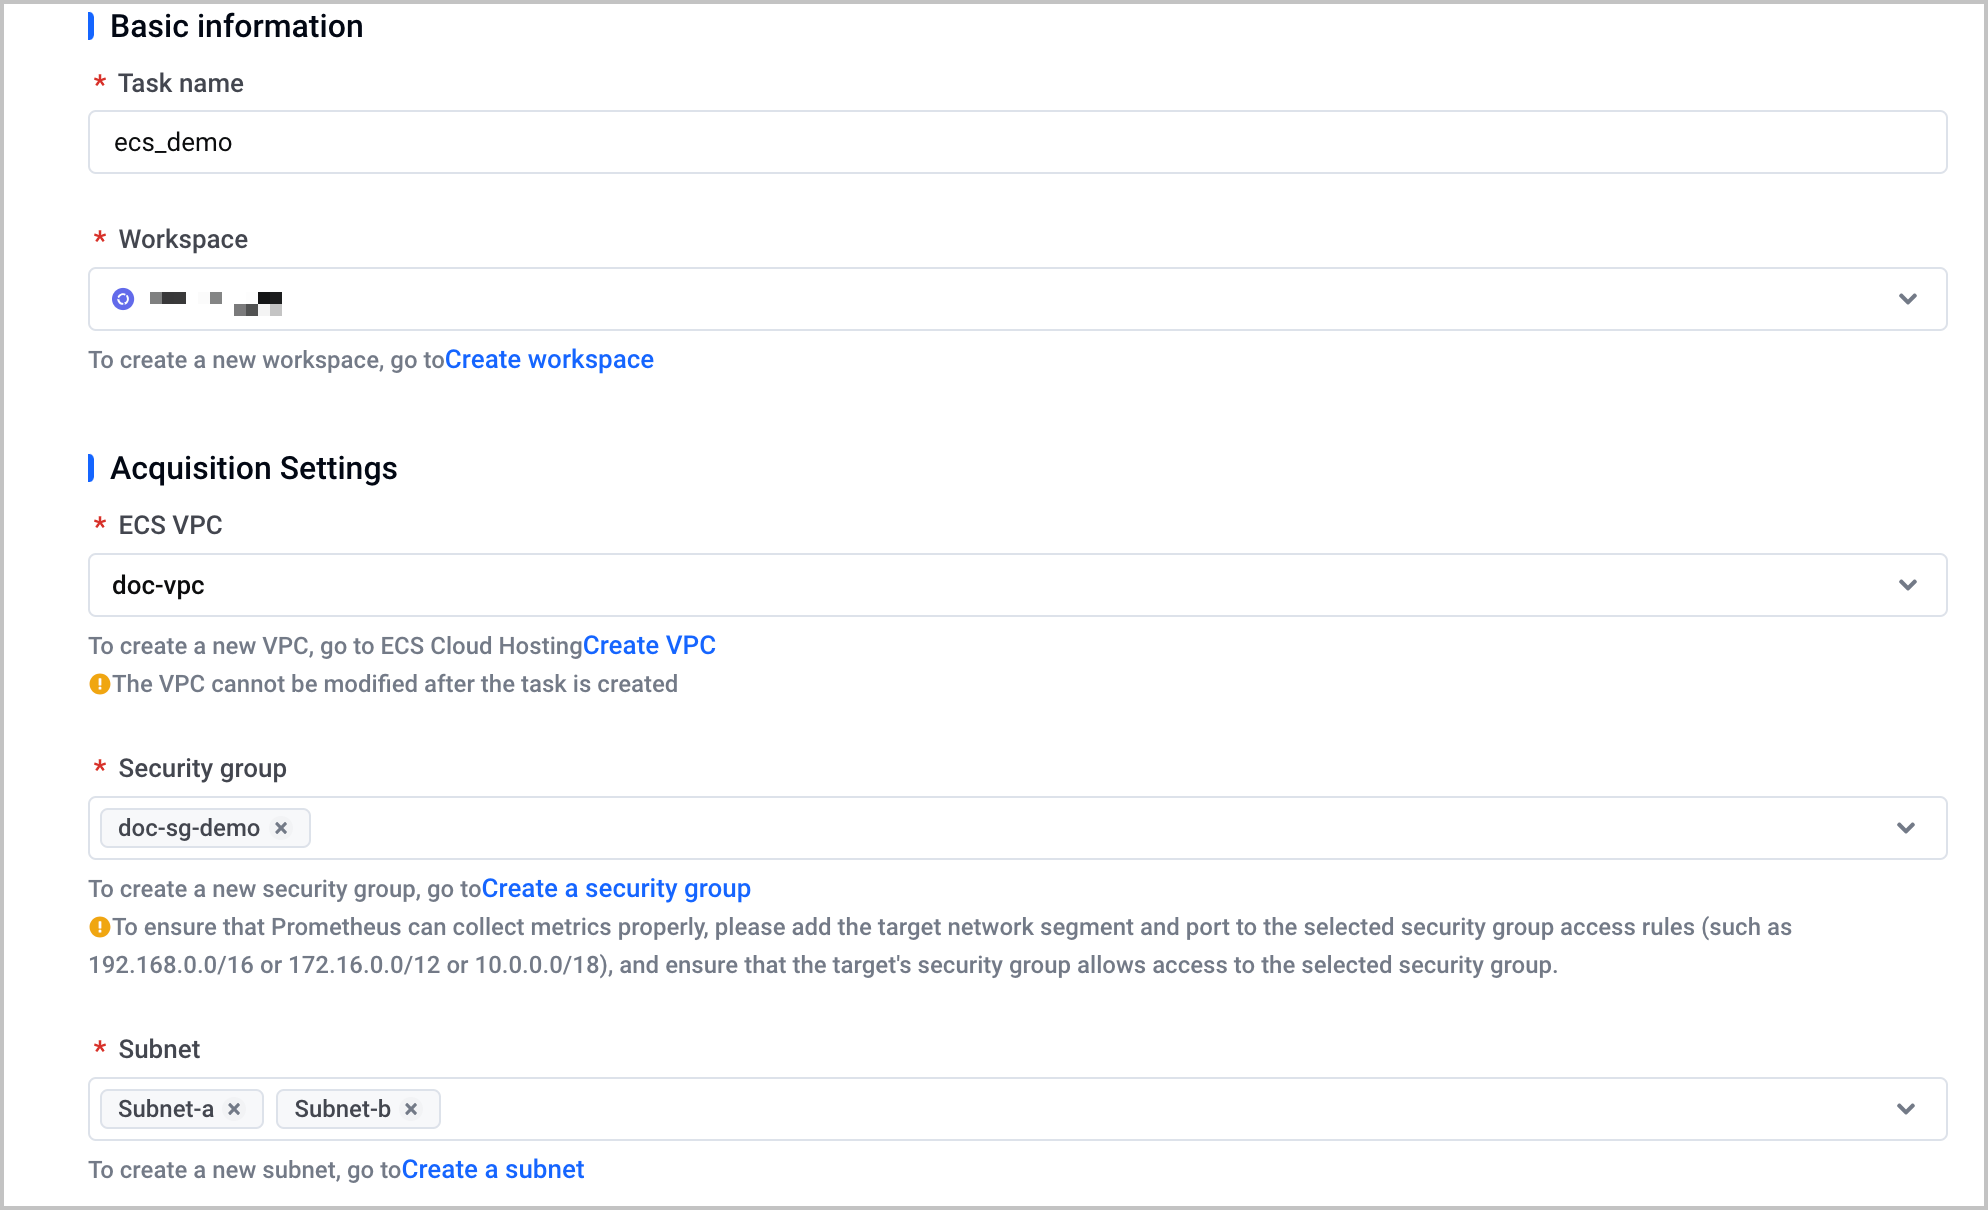
- ParameterDescriptionTask nameConfigure the name of the integration task. It can contain Chinese characters, letters (uppercase and lowercase), digits, and underscores (_), and must be 1 to 40 characters in length.workspaceSelect a created VMP workspace.ECS VPCSelect the VPC where the ECS instance is located.SubnetSelect a VPC subnet for service discovery. The system performs ECS service discovery in the selected subnet and monitors all ECS instances that meet requirements. Multiple options can be selected.
- Configure the job and specify the collection interval and the port number for service discovery.
tip
- For more parameter descriptions, refer to ECS integration.
- The Job configurations will take effect about one minute after modification and deployment. Please wait patiently.
- Click Confirm to complete the configuration.
View results
After the configuration is complete, you can view the status and details of the task. Check whether the target ECS instance is integrated with VMP properly.
- Click Integration Center in the left navigation pane and click the Integration Task tab.
- In the task list, find the target task and click Target List in the Actions column to view the ECS instances that are automatically identified by the system and integrated into VMP.
View Information
Metric
You can quickly query and display metric data by using the Explore feature of VMP. For more details, please refer to Query Metrics.
tip
Dashboard
You can build your own Grafana and view the metrics of the ECS instance and create dashboards through Grafana. It includes:
Alert
You can configure alerts for the ECS instance in the alerting center of VMP. For details, see Creating alert rules.
FAQ
How do I check whether port 9100 of ECS is occupied?
You can run the following command in the ECS console to check whether the port is occupied:
If the following information is returned, it indicates that port 9100 is already occupied.
How do I modify the default port of node-exporter?
By default, node-exporter uses port 9100 to expose metrics. When port 9100 in ECS is occupied, you can modify the --web.listen-address parameter to change the metric exposure port of node-exporter when you start node-exporter. For example, change the port to port 9200.
Last updated: 2026.10.10 11:04:51
All rights reserved © Beijing Volcano Engine Technology Co., Ltd2024
