Torch Log Service
Torch Log Service
Torch Log Service


Document
Product News
Product Overview
Product Billing
User Guide
TLS Agent
AgentLoop
Resource management
Host group
Data collection
LogCollector collection
Introduction to LogCollector
Installation and upgrade
Collect host logs
Collect container logs
LogCollector plugins
Manage LogCollector
general reference
Data import
Cloud product log collection
TOS log collection
DBW log collection
VPN Log collection
VKE log collection
CLB log collection
CloudTrail log collection
CFW log collection
NTA log collection
ALB log collection
APMPlus log collection
veFaaS log collection
VPC log collection
veImageX log collection
TrafficRoute DNS log collection
DDoS log collection
WAF log collection
DCDN log collection
Multi-cloud security platform log collection
APIG log collection
Machine learning task log collection
CR log collection
Volcano Ark application lab log collection
FileNAS log collection
LLM Application Firewall Service log collection
vePFS log collection
Cloud security center log collection
EFS log collection
Data storage
Query and analysis
Configure log indexes
Query log
Analyze logs
Query and analyze logs using third-party tools
Associate external data source for log query
SQL function
SQL syntax
Visualization
Query and analysis charts
Summaries of query and analysis charts
Create dashboard
Use dashboard
Add dashboard filters and variables
Use other systems to analyze logs
Log application
Log applications for product observability
Log applications for large models observability
Coding Agent log app
ModelProvider log app
No-coding Agent log app
Log applications for basic service monitoring
Data processing
Data transformation
Syntax and functions
Global operation function
expression function
Data processing best practices
general reference
Data write processor
Data consumer processor
Data consumption and shipping
Ship logs to TOS
Ship logs to Kafka
Ship logs to Splunk
Alarm
Alarm policy
Alarm notification content
Alarm notification content template
alarm notification channel
Tracing service
Monitor Log Service
API reference
Project management API
Topic management API
Shard management API
Index management API
Log management API
Host group management API
Collection configuration management API
Data import API
Data processor API
Data transformation API
Data backflow API
SQL analysis API
Alarm management API
Consumer group management API
Kafka protocol consumption API
Tag management API
Trace storage API
Account management API
SDK reference
Go SDK
Java SDK
Python SDK
iOS SDK
C++ SDK
CLI reference
Best practices
Data collection
Query and analysis
permission management
Consumption and delivery
Visualization
Alarm
FAQs
Billing and cost FAQ
Data collection FAQ
Data storage FAQ
Index configuration FAQ
Query and analysis FAQ
Scheduled SQL tasks FAQ
Alarm FAQ
- Documentation
 Torch Log ServiceUser GuideData consumption and shippingShip logs to TOSConfigure cross-account log shipping permissions
 Copy page
 Download PDF
Ship logs to TOS
Configure cross-account log shipping permissions
Copy pageDownload PDFConfigure cross-account log shipping permissions
If the Log Service belongs to Volcano Engine account A and Object Storage TOS belongs to Volcano Engine account B, when you need to ship data from Log Service across accounts to a TOS Bucket, create a custom role with cross-account log shipping permissions according to this document.
Configuration instructions
Create a custom role in account B and grant it the TLSShipperTosAccess policy permission. The TLSShipperTosAccess policy is a system preset policy that grants necessary permissions for Log Service to ship data to TOS. After authorization is complete, the Log Service shipping task can assume this role to ship Log Service data from account A to the TOS Bucket in account B.
tip
If account B is an IAM account, you must first grant TLSShipperTosAccess permission to account B.
Steps
- Log in to the Access Control IAM console using account B.
- Create a role.
- In the left navigation pane, click Role Management.
- On the Role Management page, click Create Role.
- In the Create Role panel, complete the following configurations.
- Set Select Trusted Entity to Account, set Select Entity to Other Account, set Account ID to account A's ID, then click Next.
- Set the role name, then click Next.
- The role name must start with TLSCrossAccount, for example, TLSCrossAccountShipTOS.
- Select the TLSShipperTosAccess permission for the role, then click Submit.
- Modify the role's trust relationship.
- On the Role Management page, click the role created in the previous step.
- Under the Trust Relationship tab, click Edit Trust Policy.
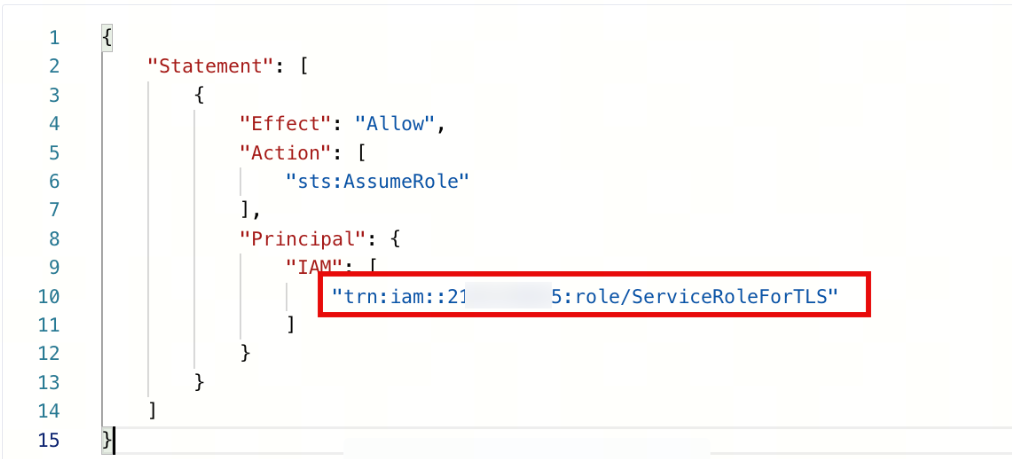
- Change the root in trn to role/ServiceRoleForTLS, then click Save.
-
- Record the role TRN.
-
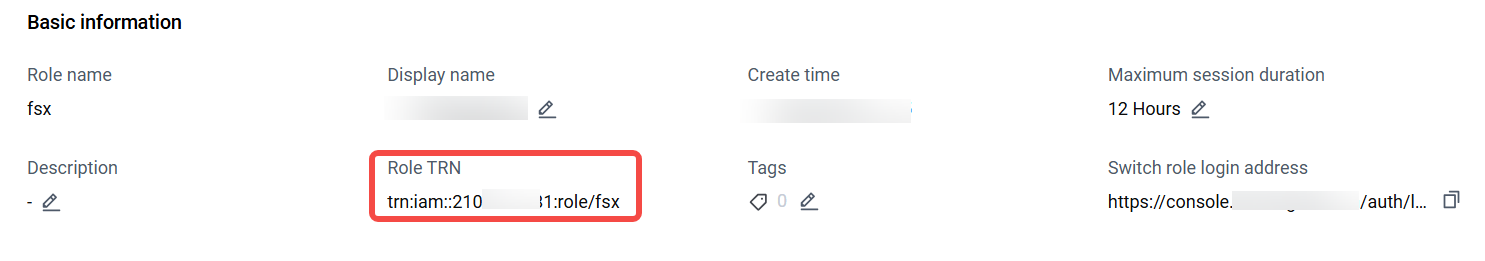
- You need to enter the role TRN when creating a cross-account delivery task. For detailed steps, see deliver in JSON format and deliver in CSV format.
-
Last updated: 2025.10.13 18:07:34
All rights reserved © Beijing Volcano Engine Technology Co., Ltd2024
