Torch Object Storage
Torch Object Storage
Torch Object Storage


Document
What's New
Announcements
Billing
Billable items
Billing method
Getting Started
User Guide
Working with buckets
Basic configurations
Managing lifecycle
Back-to-origin rules
Event notification
Intelligent Tiering
Permissions
Domain management
Fault tolerance and disaster recovery
Cross-region replication
Same-region replication
Data redundancy
Image processing
ObjectSet
Working with objects
Managing folders
Monitoring and alerting
Metric monitoring
Access control
Bucket policies
Common configuration scenarios
Authorizing IAM users of the current account
Authorizing other accounts
Managing access via tools and SDKs
Managing public read access
Data security
Access points
Multi-region access points (MRAP)
Single-region access points (SRAP)
Converged access points (CAP)
DevMind
TOS accelerator
SenseFlow
TOS Agent
Data processing
Basic concepts
Image processing
Media processing
Document preview
Task processing
Data subscription
Flow control management
Quality of Service (QoS) policies
Hierarchical namespace (HNS)
User guide
Tool reference
Best practices
TOS Vectors
User guide
API reference
Vector bucket
Vector index
SDK reference
Python-Vectors
Vector bucket
Vector index
Java-Vectors
Vector bucket
Vector index
Node.js-Vectors
Vector bucket
Vector index
Tool Guide
tosutil
Common commands
Upload, download, and copy objects
Share objects
Auxiliary commands
Common examples
TOS Browser
FSX
FSX best practices
TOS PyTorch Connector
tosfsspec
API Reference
Signature Mechanism
The header contains a signature
Bucket
Basic Bucket Operations
Bucket Lifecycle
Access Monitor
Bucket ACL
Bucket CORS
Bucket Policy
Back-to-origin Rules
Bucket Replication
Versioning
Static Website
Event Notification
Custom Domain
Server-side encryption
Transfer Acceleration
Data Processing
Image processing
Media processing
Video transcoding
Audio transcoding
video to GIF
Document preview
File decompression
Log Storage
Retention Policy
Requester pays
TLS version
Object
Basic Object Operations
Object ACL
Fetch Object
Symbolic Link
WORM object
Multipart Upload
SDK Reference
Java
Pre-signing Mechanism
Bucket Interface
Basic Bucket Interface
Manage Bucket Configuration
Object Interface
Upload Object
Download Object
Upload and Download Speed Limit
Copy Object
List Object
Data Processing
Image Processing
Video Processing
Audio Processing
Log Configuration
Hierarchical Namespace
Bucket base interface
Introduction to Typical Scenes
Python
Data processing
Pre-signature mechanism
Bucket interface
Basic bucket interface
Manage bucket configuration
Object interface
Upload object
Download object
Copy object
List objects
Introduction to typical scenes
C
Object Interface
Upload object
C++
Pre-signature Mechanism
Bucket Interface
Basic Bucket Interface
Manage Bucket Configuration
Object Interface
Upload Object
Download Object
Copy Object
List Objects
Data Processing
Go
Object Interface
Upload Object
Download Object
Copy Object
List Objects
Manage Objects
Bucket Interface
Manage Bucket Configuration
Data Processing
Log Configuration
Introduction to Typical Scenes
Pre-signature Mechanism
Node.js
Pre-signature Mechanism
Bucket Interface
Basic Bucket Interface
Manage Bucket Configuration
Object Interface
Upload object
Download object
Copy object
List objects
Data Processing
Image Processing
Introduction to Typical Scenes
Browser.js
Pre-signature Mechanism
Upload Object
Download Object
Copy Object
List Objects
Manage Objects
Data Processing
.NET
Bucket Interface
Object Interface
Upload Object
Download Object
List Objects
Introduction to Typical Scenes
PHP
Bucket Interface
Object Interface
Download Object
Data Processing
Exception Handling
Android
Bucket Interface
Object Interface
Upload Object
Download Object
Exception Handling
iOS
Bucket Interface
Object Interface
Upload Object
Download Object
Harmony
Pre-signature Mechanism
Bucket Interface
Object Interface
Upload Object
Download Object
List Objects v2
Introduction to Typical Scenarios
Rust
Pre-signing mechanism
Bucket interface
Basic bucket operations
Lifecycle rules
Bucket ACLs
Cross-origin resource sharing
Bucket inventory
Back-to-origin rules
Bucket replication
Static website hosting
Event notification
Custom domain
Server-side encryption
Object interface
Basic operation
Access control
Error Codes
01-SERVICE_ERROR
02-AUTH
03-ACCESS_CONTROL
04-QOS
05-REQUEST
06-BUCKET
07-LIFECYCLE
08-ACL
09-CORS
10-POLICY
11-MIRROR
12-REPLICATION
13-WEBSITE
14-NOTIFICATION
15-ENCRYPT
16-CUSTOMDOMAIN
17-OBJECT
18-TAG
19-MULTIPART
20-STORAGE_CLASS
21-CALLBACK
22-DATA_PROCESS
23-BATCH
24-STORAGE_LENS
25-INVENTORY
26-DIRECTORY_BUCKET
FAQ
Best Practices
AIGC-Doubao LLMs
Accessing TOS with third-party tools
Granting temporary access
Data migration
Data processing
Checking data integrity
Performance optimization
- Documentation
 Torch Object StorageUser GuideAccess controlCommon configuration scenariosAuthorizing non-owners
 Copy page
 Download PDF
Common configuration scenarios
Authorizing non-owners
Copy pageDownload PDFAuthorizing non-owners
Non-owners are users who do not own any buckets or objects. However, you can grant them permission to access these resources, including the ability to download objects. This topic explains how to authorize non-owners.
Scenario
This tutorial uses the users "aaa", "bbb", and "ccc" as examples. The background and objective are as follows:
- Background: User aaa owns the "test" bucket. User bbb has permission to upload objects to the bucket. User ccc has no permissions.
- Objective: After authorization, User ccc will be able to download objects in the "test" bucket, which are uploaded by User bbb.
Steps
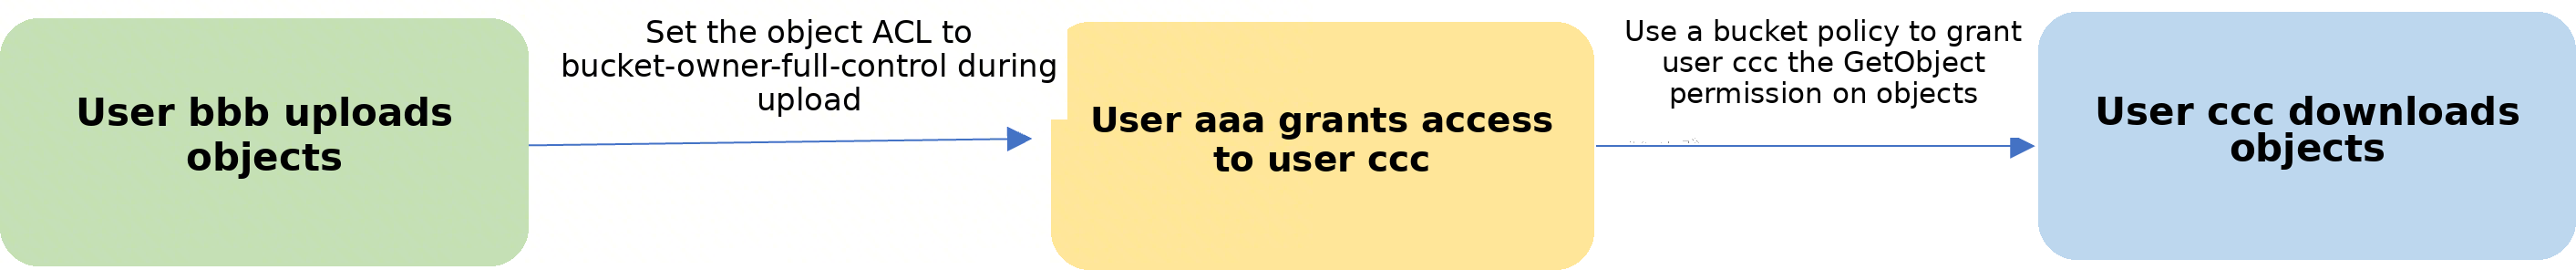
- When uploading the sample.txt object to the data directory of the "test" bucket, User bbb sets the object' access control list (ACL) permission to "bucket-owner-full-control". This grants User aaa full access to the object.
- Through a bucket policy, User aaa grants User ccc GetObject permission for the data directory of the "test" bucket. This allows User ccc to download the sample.txt object.
- For more information about bucket policies, see Overview.
Prerequisites
- A bucket has been created. For more information, see Creating buckets.
- User bbb has been granted permission to upload objects to the bucket. For more information, see Allowing an IAM user to upload and download objects in a bucket.
- tosutil has been downloaded and installed. For instructions, see Downloading and installing tosutil.
Step 1: Upload the object
- Run this command to initialize the tosutil configuration.
- ./tosutil config -i <access key> -k <secret key> -e <endpoint> -re <region>
- ParameterDescriptionParameterDescriptionaccess keyThe access key ID (AK) for User bbb.For instructions on how to view the AK and SK, see Viewing the Access Key ID and Secret Access Key.secret keyThe secret access key (SK) for User bbb.endpointTOS external access domain name.regionThe region where the "test" bucket is located.
- Run this command to upload the sample.txt object and set its ACL permission to "bucket-owner-full-control".
- ./tosutil cp file1_url tos://bucket[/prefix] -acl=bucket-owner-full-control
- Example:
- ./tosutil cp sample.txt tos://test/data/sample.txt -acl=bucket-owner-full-control
- ParameterDescriptionParameterDescriptionfile_urlThe path for a local file. To upload multiple objects, add multiple file_url values to the command and separate them with commas (,).tipYou can also use tosutil to upload folders or a list of objects. For instructions, see Upload objects (cp).bucketSpecifies the name of the bucket being reported.prefixThe prefix used for filtering objects in batch operations.-aclSets the predefined access control lists (ACLs) for objects to be uploaded or copied. Possible values:
- private: Private permission.
- public-read: Publicly readable.
- public-read-write: Publicly readable and writable.
- authenticated-read: Authenticated users have read access.
- bucket-owner-read: The bucket owner has read access.
- bucket-owner-full-control: The bucket owner has full control.
- bucket-owner-entrusted: Controlled by the bucket policy, with the bucket owner having full control.
Step 2: Allow User ccc to download the object
- Log in to the TOS console.
- In the left navigation pane, click Buckets. In the Buckets list, click the bucket you want to manage.
- In the left navigation pane, select Permissions > Bucket policies.
- Click Create policy.
- On the Create Bucket Authorization Policy page, select Custom Policy and click Next.
- Configure the following parameters.
- CategoryParameterDescriptionCategoryParameterDescriptionBasic configurationPolicy configuration methodUse the default option, i.e., Visual view.Policy nameEnter a name for the policy. The policy name must be unique within a bucket.EffectEffectSelect the effect of the policy. In this example, use the default value.
- Allow (Default): Allows the matched requests.
- Deny: Denies the matched requests.
Authorized userAuthorized userUse the default option, i.e., Specified account.Other accountsSelect Current main account. Under Sub account name, click Add Field and select User ccc from the dropdown menu.ResourceResource scopeSelect Objects in bucket and Specified object(s). Then, click Add Field and set Resource path to data/*.ActionGeneral ActionIt is optional. You can also select one or more actions you want to authorize based on your needs. For more information, see Supported actions.Bucket ActionObject ActionSelect GetObject. You can also select other actions as needed. For more information, see Object actions.Operational strategyUse the default option, i.e., Include the above actions. This option allows users to perform the specified actions.Condition (Optional)-Click the Add Field icon and set the condition and value.
- Save your settings by clicking Next.
- After verifying the details, click Create.
Step 3: Download the object
User ccc can use the GetObject API to download the sample.txt object. For more information about the GetObject API, see GetObject.
Last updated: 2026.08.14 16:23:30
All rights reserved © Beijing Volcano Engine Technology Co., Ltd2024
