Elastic Compute Service
Elastic Compute Service


Document

- Documentation
 Elastic Compute ServiceElastic Compute ServiceBest PracticesInstance configurationSetting up AD Domain Services on Windows OSSetting up AD Domain Services with multiple domain controllers
 Copy page
 Download PDF
Setting up AD Domain Services on Windows OS
Setting up AD Domain Services with multiple domain controllers
Copy pageDownload PDFSetting up AD Domain Services with multiple domain controllers
This topic uses the Windows Server 2022 Datacenter operating system as an example to describe how to deploy Windows Active Directory (AD) Domain Services with multiple domain controllers.
About AD Domain Services
AD Domain Services is a core directory service provided by Microsoft for the Windows Server operating system. Essentially, it is a centralized, hierarchical database designed to store and manage information about all resources in a network environment. Its core value lies in the unified management and authentication of users, computers, policies, and resources. This enables administrators and network users to easily locate and utilize such information, thereby achieving efficient and secure centralized management. Learn more.
Scenarios suitable for deploying multiple domain controllers:
- Medium and large-sized enterprises (with a large number of users or cross-regional operations) that require load balancing and high availability.
- Businesses that require high continuity and need to avoid single points of failure (for example, if one domain controller fails, another can take over automatically).
- Multi-site office scenarios, where deploying local domain controllers at different physical locations helps reduce authentication latency and network link load.
Prerequisites
- Purchase three ECS instances running the Windows Server operating system (Windows Server 2022 Datacenter is used in this topic). Two of them will serve as domain controllers (DCs) and one as a client. Learn more.
- Prepare the instance network environment
- Network information: A VPC is adopted as the network type in this topic, with the CIDR block set to 192.168.0.0/24.
- Domain name information: Prepare the domain name information. example.com is used as the sample domain name in this topic.
- Private IP addresses of instances:
- Private IP address of the instance serving as the primary DC: 192.168.3.126
- Private IP address of the instance serving as the secondary DC: 192.168.3.127
- Private IP address of the instance serving as the client: 192.168.3.128
Procedure
Step 1: Deploy the primary domain controller
- Follow the domain controller deployment guidelines to deploy the instance designated as the primary DC as a domain controller.
- Modify the DNS server address.
- Click "Start > Control Panel > Network and Internet > Network and Sharing Center". In the "Network and Sharing Center" window, click "network_0".
- In the "network_0 Status" window, click "Properties".
- In the "network_0 Properties" window, select "Internet Protocol Version 4 (TCP/IPv4)", and then click "Properties".
- In the "Internet Protocol Version 4 (TCP/IPv4) Properties" window, select "Use the following DNS server addresses" and enter the private IP address of the DNS server.
tip
Set "Preferred DNS server" to the private IP address of the current instance. Set "Alternate DNS server" to the private IP address of the instance designated as the secondary domain controller.
- Click the "OK" button to save the changes and exit the "network_0" properties settings.
Step 2: Deploy the secondary domain controller
- Modify the DNS server address.
- Click "Start > Control Panel > Network and Internet > Network and Sharing Center". In the "Network and Sharing Center" window, click "network_0".
- In the "network_0 Status" window, click "Properties".
- In the "network_0 Properties" window, select "Internet Protocol Version 4 (TCP/IPv4)", and then click "Properties".
- In the "Internet Protocol Version 4 (TCP/IPv4) Properties" window, select "Use the following DNS server addresses" and enter the private IP address of the DNS server.
tip
Set "Preferred DNS server" to the private IP address of the current instance. Set "Alternate DNS server" to the private IP address of the instance serving as another domain controller.
- Click the "OK" button to save the changes and exit the "network_0" properties settings.
- Execute the following command in Windows PowerShell to check whether the instance serving as the client can ping the IP address of the DNS server.
-
- Join the AD domain.
- Click "Start > Control Panel > System and Security > System". In the "Related settings" section, click "Rename this PC".
- In the pop-up "System Properties" window, click the "Change..." button.
- In the pop-up "Computer Name/Domain Changes" window, modify the computer name as needed, select "Domain" under "Member of", enter the domain name configured in your DC instance (in this topic, the domain name is example.com), and then click "OK".
- In the pop-up "Windows Security" window, enter the user name and login password of an account authorized to join the domain, then click "OK".
- If the window for confirmation pops up as below, this means that the instance has joined the domain.
- Click the "OK" button, and restart the instance to make the configuration take effect.
- After logging in to the instance again, proceed to deploy AD Domain Services.
- Click "Start > Server Manager".
- In the "Server Manager" window, click "Add roles and features".
- In the pop-up window "Add Roles and Features Wizard", click the "Next" button to open the "Select installation type" page.
- On the "Select installation type" interface, select "Role-based or feature-based installation", and then click the "Next" button.
- On the "Select destination server" page, keep the default settings and click "Next".
- On the "Select server roles" page, select "Active Directory Domain Services" and "DNS Server" in sequence.
- On the "Confirm installation selections" page, click "Install" to start the installation process.
- After the installation is complete, click "Close" to exit the wizard.
- On the "Server Manager" page, click the triangle icon in the upper right corner, and in the pop-up window, click "Promote this server to a domain controller".
- Proceed to the "Deployment Configuration" page of AD Domain Services.
- Select "Add a domain controller to an existing domain".
- Enter the domain name (in this topic, we use example.com as the domain to join).
- Click the "Change" button next to "Supply the credentials for this operation". Then in the pop-up window, enter the user name and login password of an account authorized to join the domain.
- Click the "Next" button.
- On the "Domain Controller Options" page, configure "Type the Directory Services Restore Mode (DSRM) password", then click "Next".
- On the "DNS Options" page, click the "Next" button.
- On the "Additional Options" page, click the drop-down menu next to "Replicate from" under "Specify additional replication options", select the primary domain controller, and then click "Next".
- Specify the path to store AD data, and then click the "Next" button. In the example provided in this topic, the default settings are retained.
- On the "Review Options" page, confirm the configuration information. Then, click the "Next" button.
- After the prerequisite check is passed, click the "Install" button to start installing the AD domain server. After the installation is complete, the instance will automatically restart.
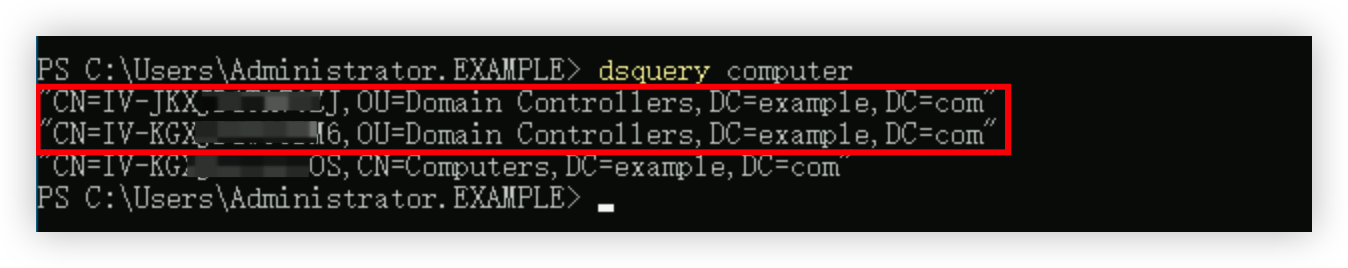
- After logging in to the instance again, execute the following command in Windows PowerShell to verify whether there are two domain controllers in the AD domain.
-
- If the following output is displayed, two domain controllers are configured in the current AD domain.
-
Step 3: Configure the client instance and add it to the AD domain
Follow the guidelines for modifying the client Security Identifier (SID) and joining the client to the AD domain to add the instance serving as the client to the AD domain.
Set "Preferred DNS server" of the client instance to the private IP address of the primary domain controller instance. Set "Alternate DNS server" to the private IP address of the secondary domain controller instance.
Last updated: 2026.06.18 17:49:53
All rights reserved © Beijing Volcano Engine Technology Co., Ltd2024
