Elastic Compute Service
Elastic Compute Service
Elastic Compute Service


Document
Elastic Compute Service
What's New
Announcement
OpenAPI related
Pricing and quotas are related
About products and plugins
Feature discontinuation
Overview
Billing
Billable items
Billing methods
Billing methods change
Getting Started
User Guide
Instances
Instance types
X86 Computing
Elastic Bare Metal Server
Heterogeneous Computing
Select instance billing method
Spot instance
Elastic Scheduled Instance
Offsetting Resources
Reserved Instances
Buying ECS instances
Logging in to an instance
Logging in to a Linux instance
Managing instance status
Modifying instance types
Using instance user data and metadata
Instance metadata
Images
Public images
veLinux images
Custom images
Importing custom images
Creating custom images
Image detection
End of life (EOL) of image
Elastic Block Storage
Basic volume operations
Partitioning and formatting a volume
Extending a volume
EBS Agent
Snapshots
Basic snapshot operations
Auto snapshot policies
DataInsights
Network
Network interface and IP address
IP Address
IPv4 address
Security group
Security
Passwords and key pairs
Deployment and scaling
Monitoring
Monitoring metrics
Event monitoring
Local volume event O&M
Method 1: Solve the local volume failure by replacing the faulty volume
O&M
Cloud assistant
Managing agents
Process choreography
Common operation and maintenance tasks
Batch operations on instances
Batch operations on EBS Volumes
Batch operations on images
Temporary upgrade of bandwidth
Managing application updates
orchestration plan
Patch management
Managing patch plans
Managing patch baselines
IAM
Tags and projects
Best Practices
AI applications
OpenClaw (formerly Moltbot)
Quickly deploying OpenClaw via application templates
Quickly deploying OpenClaw via marketplace images
Manually deploying OpenClaw
Self-service website creation
Building environments
Building a Web environment (Windows)
Building applications
Building FTP site
Deploying databases
Building game servers
Building websites
Building a WordPress blog
Building multiple websites
Manage software sources for Linux instances
AIGC practices
Performance test
Network performance test
Instance configuration
Setting up AD Domain Services on Windows OS
Windows Multi - User Login
Changing screen resolution
Instance data
Uploading or downloading files
Data restoration
ECS instance local time synchronization
Volume
Monitoring
Security
Images
Kernel fine-tuning
O&M
Troubleshooting
Remote log in issue
Linux operating system issue
Windows operating system issue
SSH log in issue
Operating system issue
veLinux operating system issue
Linux operating system issue
Windows operating system issue
Instance status issue
Instance unable to start issue
High instance load issue
GPU instances issue
Network connection issue
Network configuration issue
Storage classes issue
EBS Volume issue
Local Disk issue
Logs and monitoring issue
Third - party software issue
API Reference
Regions and availability zones
Instances
Images
HPC clusters
Key pairs
Tags
Volumes
Reserved storage capacity
Snapshot
Auto snapshot policy
Monitoring
Deployment sets
Launch templates
Cloud assistant
Patch management
SDK reference
CLI Reference
FAQ
Dedicated Host DDH
What's New
Billing
User Guide
Manage Dedicated Host
Manage Dedicated Host Cluster
Manage ECS instances
Monitoring and O&M
API reference
proprietary host
- Documentation
 Elastic Compute ServiceElastic Compute ServiceBest PracticesSelf-service website creationBuilding applicationsBuilding FTP siteSetting up FTP sites (Ubuntu 22.04)
 Copy page
 Download PDF
Building FTP site
Setting up FTP sites (Ubuntu 22.04)
Copy pageDownload PDFSetting up FTP sites (Ubuntu 22.04)
FTP is an application-layer protocol used for file transfer between a client and a server over a computer network. Typically, it operates on two ports: 20 and 21. This topic describes how to set up an FTP site on a Ubuntu 22.04 instance.
Prerequisites
- You have purchased an ECS instance and associated an EIP with it.
- The ECS instance status is Running.
Software version
- Linux operating system: This topic uses Ubuntu 22.04 as an example.
- Client operating system: This topic uses macOS Sequoia 15.6.1 as an example.
- vsftpd: This topic uses vsftpd 3.0.2 as an example.
Procedure
Step 1: Install vsftpd
- Log in to the ECS console.
- Execute the following commands to install vsftpd.
- sudo apt-get updatesudo apt-get -y install vsftpd
- Execute the following command to specify that the vsftpd automatically starts upon instance startup.
- systemctl enable vsftpd
- Execute the following command to start the FTP service.
- systemctl start vsftpd
- Execute the following command to check whether the service is started.
- netstat -antup | grep vsftpd
- If the following output is displayed, the vsftpd service is started.
-

tip
vsftpd allows anonymous access by default. The default FTP server path for anonymous users is /var/ftp/pub. Anonymous users only have view permissions—they cannot create, delete, or modify files or directories.
Step 2: Configure vsftpd
- Execute the following command to back up the vsftpd configuration file.
- sudo cp /etc/vsftpd.conf /etc/vsftpd.conf.bak
- Modify the vsftpd configuration file.
- Execute the following command to open the vsftpd configuration file.
- sudo vim /etc/vsftpd.conf
- Press the i key to enter edit mode. Enable IPv4 socket listening, and disable IPv6 socket listening.
- listen=YESlisten_ipv6=NO
- Modify the FTP access permissions to allow only local users to access FTP and disable anonymous access.
- anonymous_enable=NOlocal_enable=YES
- Modify the following configuration to enable file uploads.
- write_enable=YES
- Remove the comment symbol # at the beginning of the following configuration lines. This allows you to restrict FTP user directory access using chroot jails and configure which files FTP service users can access.
- chroot_local_user=YESchroot_list_enable=YESchroot_list_file=/etc/vsftpd.chroot_list
- Add FTP service directory configuration and enable write permissions for users in the mounted chroot (root directory change) environment.
- local_root=/home/ftp allow_writeable_chroot=YES
- Add the following configuration as needed to set FTP to active mode or passive mode.
tip
Due to firewall settings on most clients and other factors, the active mode may cause issues. We recommend using passive mode to set up an FTP service.
- Active mode
- port_enable=YES
- Passive mode
tip
Replace <PUBLIC_IP> with the actual public IP address of the server hosting the FTP site.
- pasv_enable=YESpasv_min_port=35000pasv_max_port=40000pasv_address=<PUBLIC_IP>
- Press the esc key to exit edit mode, enter :wq, and press the Enter key to save the changes and exit the configuration file.
- Create a chroot_list file, and add the list of exception usernames to the file.
tip
Users in an exception list are not restricted to their home directories and can access other directories.
- Execute the following command to create the chroot_list file.
- sudo vim /etc/vsftpd.chroot_list
- Press i to enter edit mode and enter the exception user list.
- Press Esc to exit the edit mode, enter :wq, and then press Enter to save and exit the file.
- Execute the following command to restart vsftpd for the configuration to take effect.
- sudo systemctl restart vsftpd
Step 3: Configure user directory
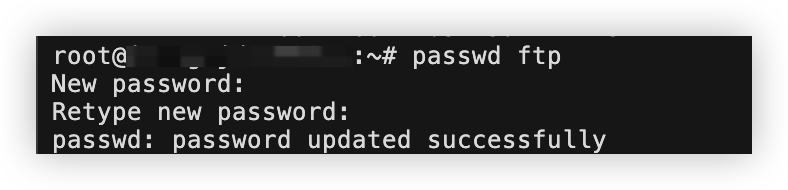
- After you install vsftpd, a default passwordless user named ftp is created. Execute the following command to modify the password.
- sudo passwd ftp
- If the following output is displayed, the login password for user ftp is modified.
-
- Execute the following command to ensure that the shell of user ftp is included in the /etc/shells file.
- SHELL_TO_CHECK=$(getent passwd ftp | cut -d: -f7) && (grep -q "^$SHELL_TO_CHECK$" /etc/shells || echo "$SHELL_TO_CHECK" >> /etc/shells)
- Execute the following command to add the user ftp to the vsftpd list of users allowed to log in.
- echo "ftp" | sudo tee -a /etc/vsftpd.userlist
- Execute the following command to create the FTP file directory.
- sudo mkdir /home/ftp
- Execute the following command to grant permissions for the FTP file directory.
tip
In the example provided in this topic, read, write, and full control permissions on the folder are granted. Modify the corresponding permissions as needed.
- sudo chmod 777 /home/ftp
Step 4: Configure security group
After the FTP site is set up, add rules to the inbound direction of the instance security group and allow the following FTP ports. For detailed steps, refer to Changing security group rules.
FTP usage mode | Direction | Protocol type | Port range | Source address |
FTP usage mode | Direction | Protocol type | Port range | Source address |
Active mode | Inbound | TCP | 20/21 | 0.0.0.0/0 |
Passive mode | Inbound | TCP | Port 21, and all ports between the values of parameters pasv_min_port and pasv_max_port, which are defined in the /etc/vsftpd/vsftpd.conf configuration file. tip To adjust the passive mode port range, refer to configuration recommendations. This topic uses the range 35000-40000 as an example. | 0.0.0.0/0 |
Step 5: Client test
You can verify the FTP service using FTP client software, a browser, a file explorer, or other tools. This topic uses MacOS Finder as an example.
- Open Finder and select "Go > Connect to Server" in the top menu bar.
- Enter ftp://ECS instance EIP:21 and click the "Connect" button.
- In the pop-up login window, confirm the FTP server information and click the "Connect" button.
- Enter the FTP username and password that have been set, and then click "Connect". After the connection succeeds, you can view the files in the specified directory on the FTP server.
warning
Since macOS "Finder" does not support uploading files to an FTP server, you can download third-party software like FileZilla to transfer files.
Last updated: 2026.06.18 17:48:27
All rights reserved © Beijing Volcano Engine Technology Co., Ltd2024
