Volcengine Kubernetes Engine
Volcengine Kubernetes Engine
Volcengine Kubernetes Engine


Document
Volcengine Kubernetes Engine
What's New
History feature release notes
Kubernetes version release notes
Containerd runtime release notes
Add-on release notes
Monitoring add-ons
Scheduling add-ons
DNS add-ons
Security add-ons
GPU add-ons
Sandbox add-on
Security announcements
Product Announcement
Historical announcements
Overview
Getting started
User guide
Clusters
Creating clusters
Connecting to clusters
Upgrading clusters
Node pool
Creating node pools
Scaling out/in node pools
Nodes
Authorization management
Image
Namespaces
Networking
Cluster network
Container Network
Service
LoadBalancer
CLB
Ingress
APIG Ingress
ALB Ingress
Customize ALB Ingress forwarding rules
Certificate and security
CLB Ingress
Nginx Ingress
Gateway API
Workloads
Creating workloads
Configure workloads
Pods
Configuration management
Image acceleration
Storage
FSX client
EBS Volumes
TOS Volumes
NAS volumes
FSX access methods
NFS access methods
EFS volumes
vePFS volumes
FSX access methods
vePFS Client access methods
NFS access methods
CloudFS volumes
Local volumes
Autoscale
Node autoscaler
Workload autoscaler
Horizontal Pod Autoscaler (HPA)
Cron Horizontal Pod Autoscaler (CronHPA)
Intelligent Horizontal Pod Autoscaler (IHPA)
Horizontal Pod Autoscaler based on event-driven (KEDA)
Add-on management
Network add-ons
Storage add-ons
Monitoring add-ons
Scheduling add-ons
DNS add-ons
GPU add-ons
Core add-ons
Sandbox add-on
Upgrading add-ons
Heterogeneous computing
NVIDIA GPU
mGPU scheduling
RDMA high-performance computing
Scheduling management
Topology-aware scheduling
QoS-aware scheduling
Observability
Log management
Basic observation
Setup & Configuration
Cluster observation
Storage observation
Other observation
Using metrics
Full stack observation
Alert management
Diagnosis and inspection
Node check and self-healing
Application center
Backup center
Stability
Large-scale cluster management
Best practices
Authorization
Clusters
Nodes and node pools
Networking
Storage
Scheduling
Observability
Solution
Security and compliance
API reference
Cluster management
NodePool management
Node management
Virtual nodes management
Add-on management
Tag management
Access policy management
Instance images management
Cloud native observability
Inspection and diagnosis
Task management
Volcengine Container Instance
Appendix
SDK reference
Development guide
Terraform
FAQs
General FAQs
Cluster FAQ
cluster management
cluster network
cluster upgrade
Node and Node pool FAQs
Authorization FAQs
Workload FAQs
Service and Ingress FAQs
Storage FAQs
Heterogeneous computing FAQs
Observability FAQs
Quota FAQs
Add-on FAQs
Cloud-native AI
ServingKit
LLM applications
ComfyUI application
Deploying the Al inference application through Helm
Deepseek practices
Qwen practices
Kimi practice
Seed practices
Best practices
DeepSeek model deployment
GLM model deployment
MiniMax model deployment
Qwen model deployment
Kimi model deployment
Volcengine Container Instance
What's new
Historical feature release notes
Product Announcement
Overview
Billing
User guide
Integrating with VCI
Virtual node
VKE cluster uses virtual nodes
Self-managed/third-party cluster uses virtual node
Creating an instance
General purpose instance
GPU-accelerated computing instance
VCI Agent Sandbox
Startup acceleration
E2B-based management
Upgrade guide
Networking
Monitoring
Scheduling
Container configuration
VCI Image Cache
Best practices
Security and compliance
FAQs
- Documentation
 Volcengine Kubernetes EngineVolcengine Kubernetes EngineSecurity and complianceShared security responsibility for VKE
 Copy page
 Download PDF
Security and compliance
Shared security responsibility for VKE
Copy pageDownload PDFShared security responsibility for VKE
This topic describes the shared security and compliance responsibility model for the architecture of managed VKE clusters.
Compared with traditional on-premises data centers, cloud computing separates service operators from customers, offering greater flexibility and control while effectively reducing operational burdens on customers. Therefore, cloud computing security cannot be fully borne by a single party. Cloud security requires joint efforts from Volcano Engine and you.
Security responsibility division
Volcano Engine responsibilities
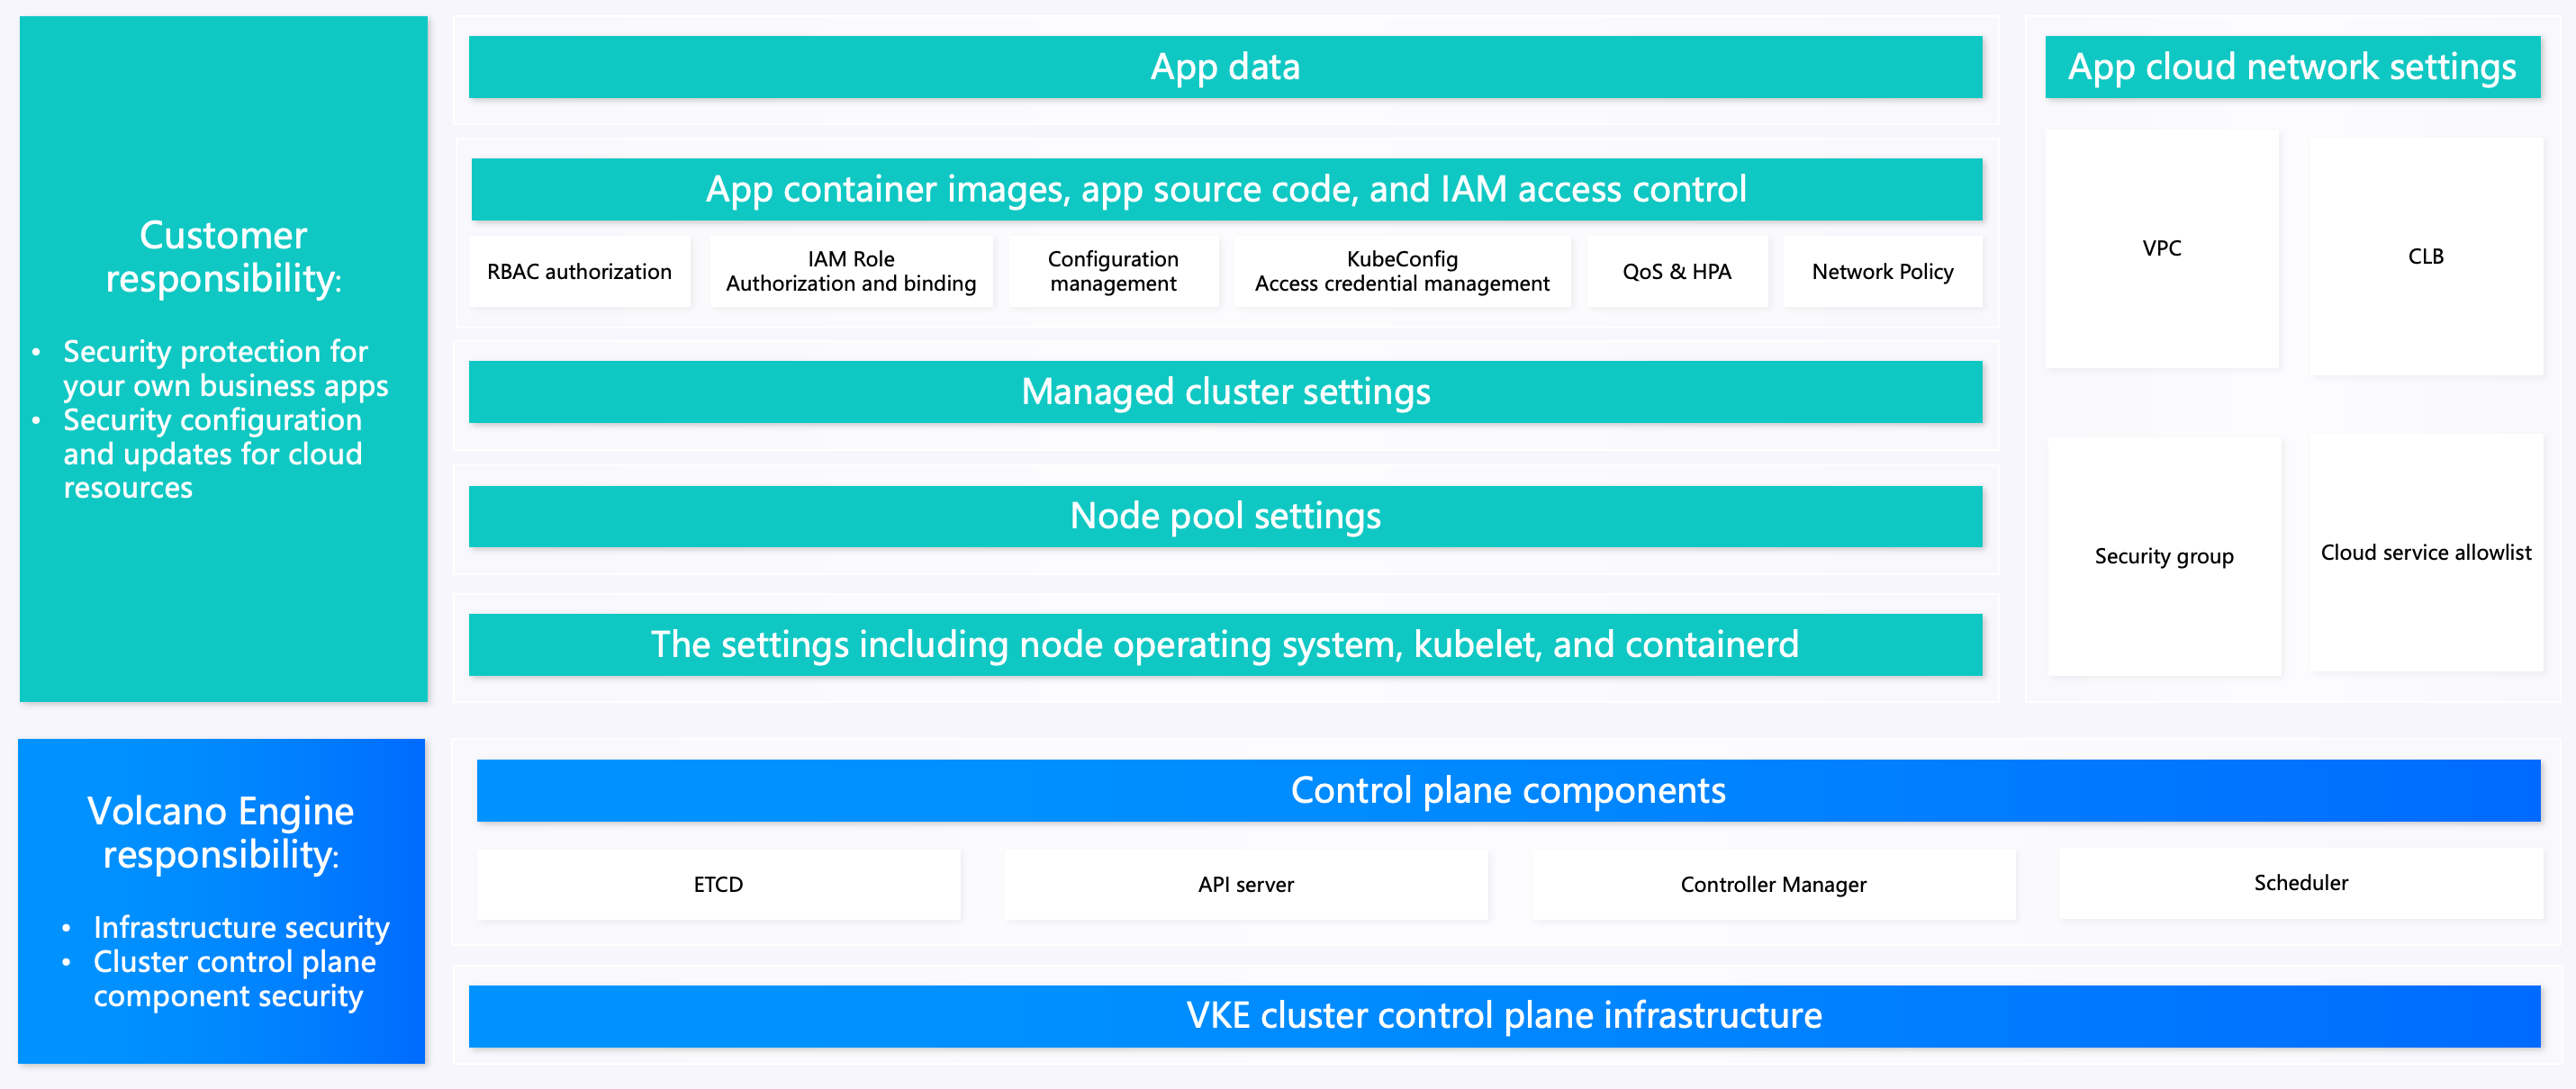
On the control plane side, Volcano Engine leverages comprehensive platform security capabilities to ensure the security of control plane infrastructure, including cloud service resources such as computing, storage, and networking. Meanwhile, based on universal Volcano Engine security baseline standards (such as operating system security hardening), Volcano Engine implements standard-aligned security hardening for VKE cluster control plane component configurations and images. For security vulnerabilities at the node operating system or Kubernetes component level, Volcano Engine is responsible for promptly issuing relevant announcements and providing corresponding vulnerability patches or version update capabilities.
Your responsibilities
Your security and operations team is responsible for the security protection of business applications deployed on the cloud, as well as the security configuration and update of cloud resources. Specific responsibilities are as follows:
- Based on Volcano Engine announcements and the provided patch or version upgrade methods, promptly repair vulnerabilities and update versions of operating systems, cluster system add-ons, and cluster runtimes. Based on Volcano Engine announcements and the provided patch or version upgrade methods, promptly repair vulnerabilities and update versions of operating systems, cluster system add-ons, and cluster runtimes.
- Configure parameters related to VKE clusters, node pools, and networks in accordance with the security principles to prevent attackers from exploiting improper parameter or permission configurations.
- Perform application authorization, account or role authorization, and credential management in accordance with the principle of least privilege.
- Implement and deploy security policies based on usage requirements, and ensure the security of application parameter settings.
- Ensure the supply chain security of artifacts such as container images required for application deployment.
- Ensure the security of application data and applications.
- Delete IAM users or roles associated with resigned employees or untrusted personnel, and revoke the corresponding KubeConfig credentials. For specific operations, see Managing access credentials.
Understanding the shared responsibility model
Before designing and deploying enterprise application systems, understand the security responsibility boundaries between you and Volcano Engine.
The shared cluster security responsibility model for VKE cluster management architecture is shown in the following figure.
Related documentation
Last updated: 2026.10.16 17:40:20
All rights reserved © Beijing Volcano Engine Technology Co., Ltd2024
