Volcengine Kubernetes Engine
Volcengine Kubernetes Engine
Volcengine Kubernetes Engine


Document
Volcengine Kubernetes Engine
What's New
History feature release notes
Kubernetes version release notes
Containerd runtime release notes
Add-on release notes
Monitoring add-ons
Scheduling add-ons
DNS add-ons
Security add-ons
GPU add-ons
Sandbox add-on
Security announcements
Product Announcement
Historical announcements
Overview
Getting started
User guide
Clusters
Creating clusters
Connecting to clusters
Upgrading clusters
Node pool
Creating node pools
Scaling out/in node pools
Nodes
Authorization management
Image
Namespaces
Networking
Cluster network
Container Network
Service
LoadBalancer
CLB
Ingress
APIG Ingress
ALB Ingress
Customize ALB Ingress forwarding rules
Certificate and security
CLB Ingress
Nginx Ingress
Gateway API
Workloads
Creating workloads
Configure workloads
Pods
Configuration management
Image acceleration
Storage
FSX client
EBS Volumes
TOS Volumes
NAS volumes
FSX access methods
NFS access methods
EFS volumes
vePFS volumes
FSX access methods
vePFS Client access methods
NFS access methods
CloudFS volumes
Local volumes
Autoscale
Node autoscaler
Workload autoscaler
Horizontal Pod Autoscaler (HPA)
Cron Horizontal Pod Autoscaler (CronHPA)
Intelligent Horizontal Pod Autoscaler (IHPA)
Horizontal Pod Autoscaler based on event-driven (KEDA)
Add-on management
Network add-ons
Storage add-ons
Monitoring add-ons
Scheduling add-ons
DNS add-ons
GPU add-ons
Core add-ons
Sandbox add-on
Upgrading add-ons
Heterogeneous computing
NVIDIA GPU
mGPU scheduling
RDMA high-performance computing
Scheduling management
Topology-aware scheduling
QoS-aware scheduling
Observability
Log management
Basic observation
Setup & Configuration
Cluster observation
Storage observation
Other observation
Using metrics
Full stack observation
Alert management
Diagnosis and inspection
Node check and self-healing
Application center
Backup center
Stability
Large-scale cluster management
Best practices
Authorization
Clusters
Nodes and node pools
Networking
Storage
Scheduling
Observability
Solution
Security and compliance
API reference
Cluster management
NodePool management
Node management
Virtual nodes management
Add-on management
Tag management
Access policy management
Instance images management
Cloud native observability
Inspection and diagnosis
Task management
Volcengine Container Instance
Appendix
SDK reference
Development guide
Terraform
FAQs
General FAQs
Cluster FAQ
cluster management
cluster network
cluster upgrade
Node and Node pool FAQs
Authorization FAQs
Workload FAQs
Service and Ingress FAQs
Storage FAQs
Heterogeneous computing FAQs
Observability FAQs
Quota FAQs
Add-on FAQs
Cloud-native AI
ServingKit
LLM applications
ComfyUI application
Deploying the Al inference application through Helm
Deepseek practices
Qwen practices
Kimi practice
Seed practices
Best practices
DeepSeek model deployment
GLM model deployment
MiniMax model deployment
Qwen model deployment
Kimi model deployment
Volcengine Container Instance
What's new
Historical feature release notes
Product Announcement
Overview
Billing
User guide
Integrating with VCI
Virtual node
VKE cluster uses virtual nodes
Self-managed/third-party cluster uses virtual node
Creating an instance
General purpose instance
GPU-accelerated computing instance
VCI Agent Sandbox
Startup acceleration
E2B-based management
Upgrade guide
Networking
Monitoring
Scheduling
Container configuration
VCI Image Cache
Best practices
Security and compliance
FAQs
- Documentation
 Volcengine Kubernetes EngineVolcengine Kubernetes EngineUser guideNetworkingDNSUsing NodeLocal DNSCache as a DNS caching proxy
 Copy page
 Download PDF
DNS
Using NodeLocal DNSCache as a DNS caching proxy
Copy pageDownload PDFUsing NodeLocal DNSCache as a DNS caching proxy
NodeLocal DNSCache cache solution provides a DNS cache proxy for nodes, improving DNS service discovery performance and stability across the entire cluster. This topic describes how to configure NodeLocal DNSCache in a cluster.
Background information
In large-scale applications, overwhelming DNS requests place significant pressure on CoreDNS, resulting in increased DNS latency and adversely affecting business performance. To improve performance, users often need to upgrade CoreDNS specifications or perform scale-out, which increases operation and maintenance complexity, yet delivers a disappointing result.
To address the above issues, Kubernetes officially provides the NodeLocal DNSCache solution, which can effectively improve DNS performance and stability in large-scale clusters. In a VKE cluster, the node-local-dns add-on can be used as the NodeLocal DNSCache for the cluster. This add-on runs in a DaemonSet on each node in the cluster, working as a DNS cache proxy on nodes to improve the performance and stability of DNS service discovery in the cluster.
DNS cache configuration is injected into pods as soon as node-local-dns add-on is installed in the cluster. After that, the DNS resolution will take the following steps:
- NodeLocal DNSCache resolution: Pods first send queries to NodeLocal DNSCache (169.254.20.10) on their nodes. If NodeLocal DNSCache is unreachable or a cache miss occurs, the queries are sent to CoreDNS in the cluster.
- CoreDNS resolution: If NodeLocal DNSCache does not have a cached response for the query, the query is sent to CoreDNS (10.0.0.10) through the kube-dns service for resolution.
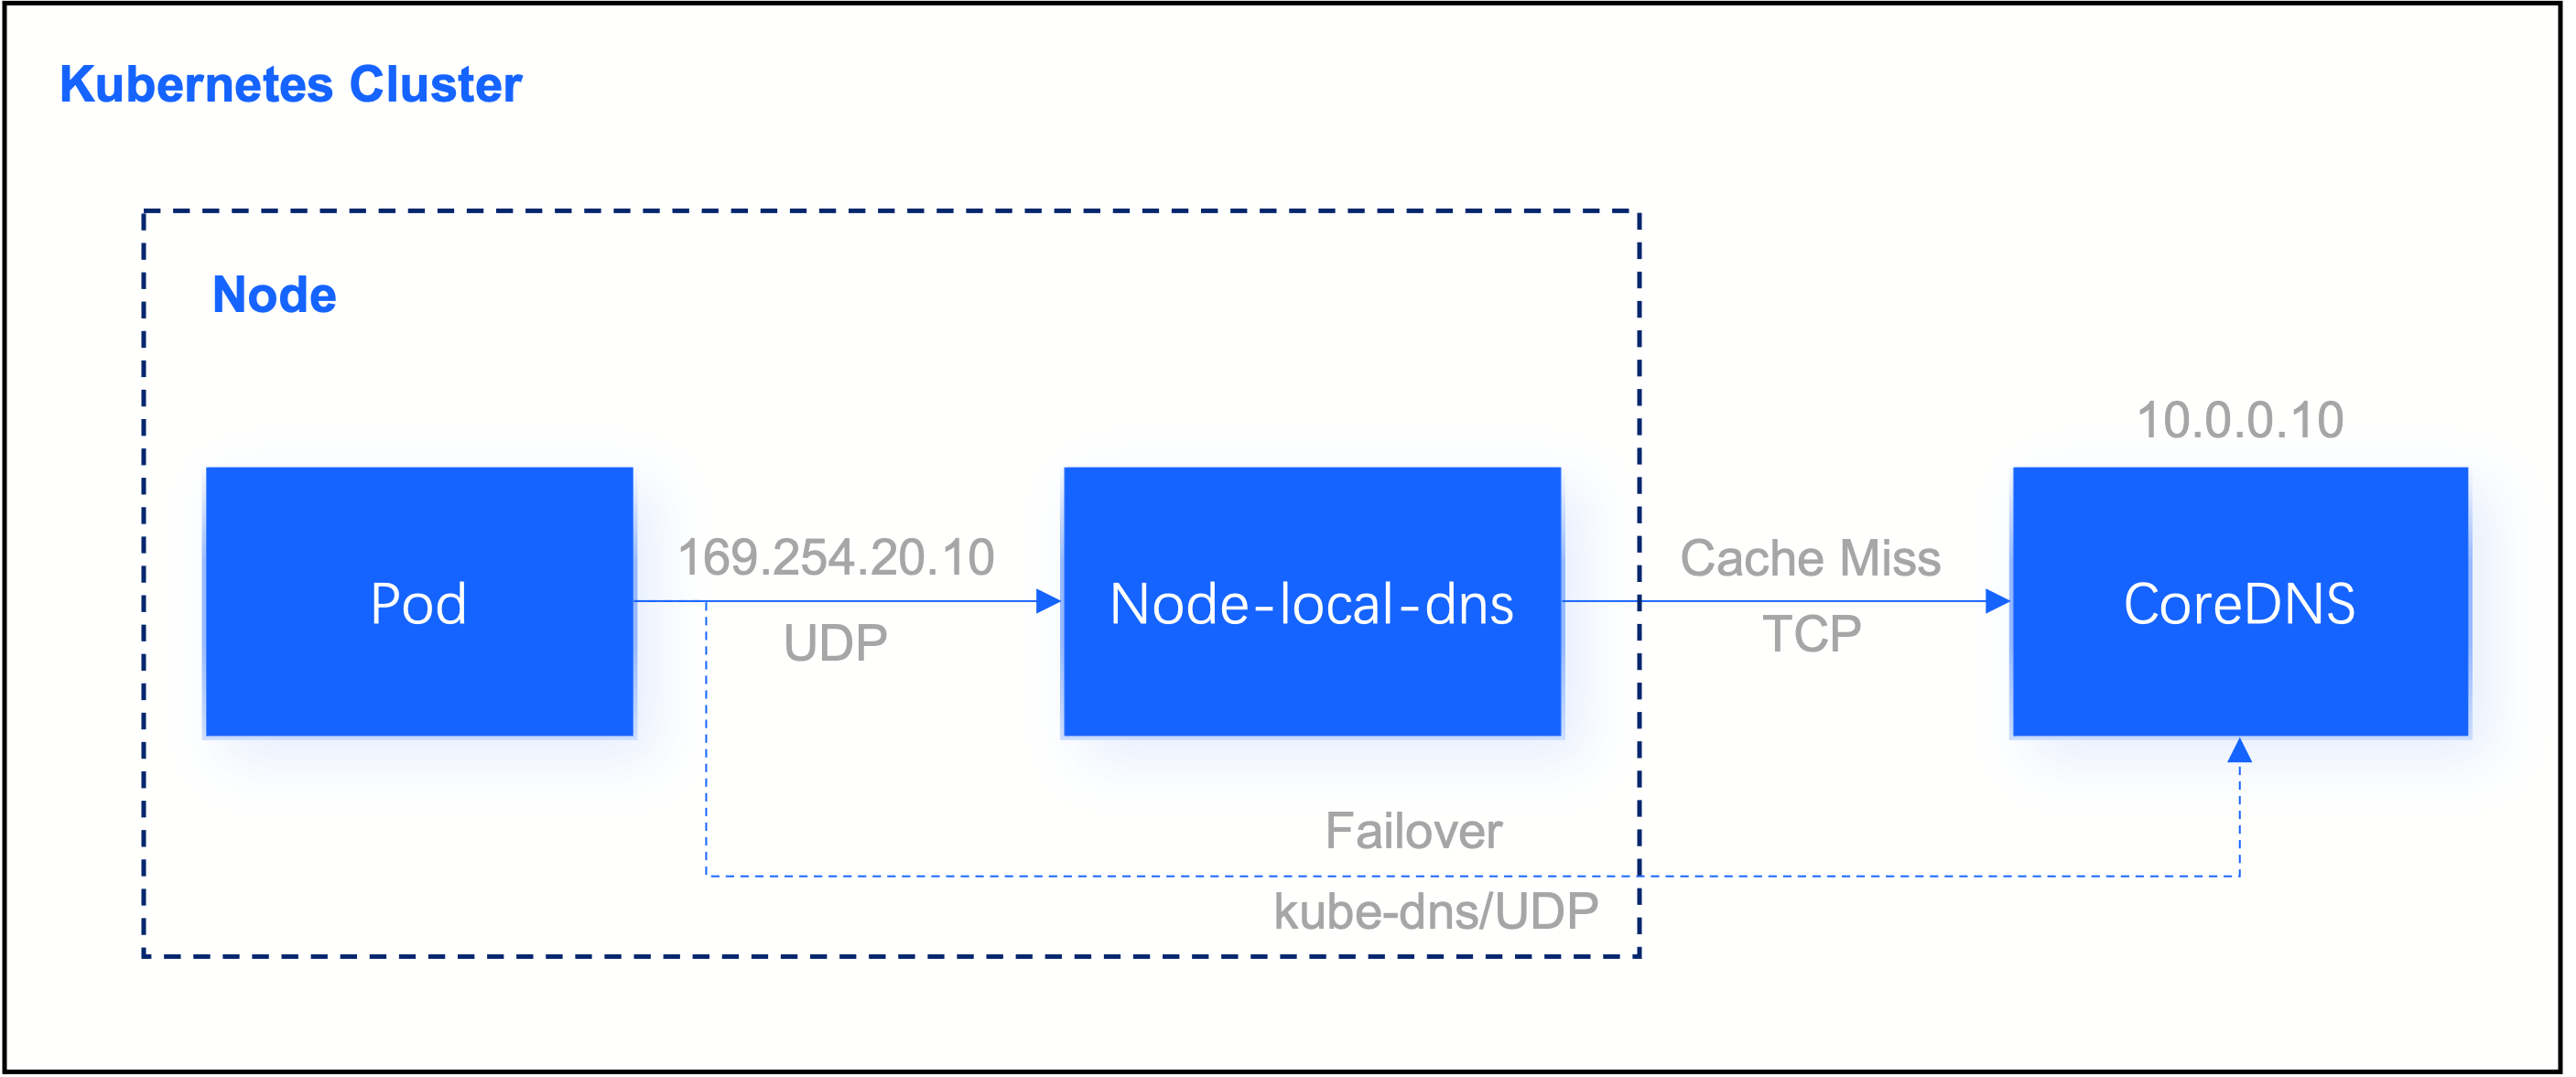
tip
Limits
- When a VCI-type Pod uses the NodeLocal DNSCache feature, the node-local-dns add-on must first be upgraded to v0.3.1 or later. For details, see Add-on release record.
- NodeLocal DNSCache requires the vpc-cni add-on v1.3.0 or later. For details, see Add-on release records.
- After the node-local-dns add-on is installed in the cluster and NodeLocal DNSCache is enabled, NodeLocal DNSCache takes effect only for newly created Pods.
Prerequisites
Application scenarios
Scenario 1: Use automatic injection
After node-local-dns add-on is installed, the newly created pods in a cluster will be injected with the dnsConfig settings by the system to enable access to NodeLocal DNSCache.
Except for the following types of pods:
- Pods belong to the kube-system and kube-public namespaces.
- Pods with namespaces or labels that contain dns-config-injection=disable.
- Pods that are running on hostNetwork and have DNSPolicy set to ClusterFirstWithHostNet, or those not running on hostNetwork and have DNSPolicy set to ClusterFirst.
Taking the pods with the default namespace as an example, the following dnsConfig settings are injected by the system.
...
dnsConfig:
nameservers:
- 169.254.20.10
- 10.0.10.1
options:
- name: ndots
value: "3"
- name: attempts
value: "2"
- name: timeout
value: "1"
searches:
- default.svc.cluster.local
- svc.cluster.local
- cluster.local
dnsPolicy: None
...
To ensure maximum availability of DNS service, the ClusterIP address (10.0.10.1) of kube-dns will also be added to the nameservers as a backup DNS server.
Scenario 2: Disable automatic injection
If necessary, you can disable NodeLocal DNSCache with the following methods.
Namespace dimension
Pod dimension
Execute the following command to disable the dnsConfig setting for all newly created pods in the specified namespace.
kubectl label namespace <namespace name> dns-config-injection=disable
Add the following label to pods to disable their dnsConfig settings.
···
labels:
dns-config-injection: disable
···
Scenario 3: Configure manually
You can configure NodeLocal DNSCache if the automatic injection does not meet your requirements. Procedure:
- For how to disable automatic injection to pods, see Disabli automatic injection.
- Manually configure NodeLocal DNSCache for pods. The following are example settings for the pods in the default namespace.
- apiVersion: v1kind: Podmetadata:name: nginxspec:containers:- image: nginx:latestname: container-0dnsPolicy: NonednsConfig:nameservers: ["169.254.20.10","172.21.0.10"] # DNS server IP addressessearches: # Complete domain names to be used when only partial domain names are found in requests- default.svc.cluster.local- svc.cluster.local- cluster.localoptions:- name: ndots # Metric to determine if a domain name is complete. If the number of dots in a domain name exceeds the value, DNS resolution starts immediately. If the number of dots in a domain name is less than the value, the domains under the searches are used accordingly to fulfill DNS resolution.value: "3"- name: attempts # Number of retry attempts when the DNS resolution failsvalue: "2"- name: timeout # Timeout for a single DNS resolution request, measured in secondsvalue: "1"imagePullSecrets:- name: default-secret...
tip
You can also use kubelet with the --cluster-dns and --cluster-domain parameters to globally control pod dnsConfig. However, this is not a recommended method. If you find it necessary to use that method, you can submit a ticket for consultation.
Related documentation
Last updated: 2026.10.12 11:09:53
All rights reserved © Beijing Volcano Engine Technology Co., Ltd2024
